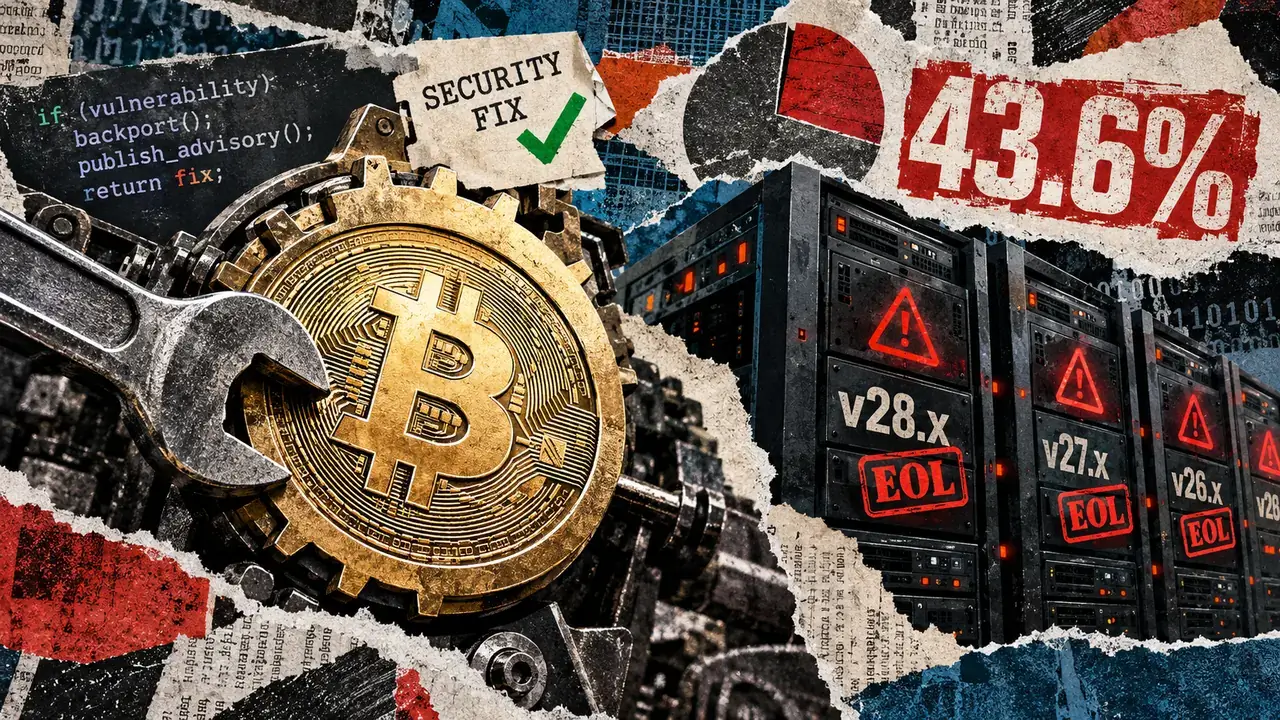
Bitcoin Core merged a policy amendment on October 22 that accelerates the release of security fixes for easily rediscoverable vulnerabilities across all maintained release lines, accompanied by public advisories.
The change addresses a growing challenge: a network snapshot from October 18 shows that 3,671 of 8,422 self-reported Bitcoin Core peers (43.6%) ran release lines that had reached end of life. The data comes from connected public peers monitored by the Karlsruhe Institute of Technology's Bitcoin network monitor.
Why the Policy Changed
Under the previous policy, medium- and high-severity vulnerabilities remained under embargo until two weeks after the last affected release reached end of life—sometimes extending a year between the fix and public disclosure. This lengthy embargo discouraged developers from openly backporting fixes, since the backport itself could reveal the vulnerability.
The new approach marks certain flaws as easily discoverable during triage, based on how readily they can be found or rediscovered, including by artificial intelligence systems. These fixes now roll out to all maintained major release lines through point releases, with advisories published simultaneously.
Bitcoin Core developers acknowledged a tradeoff: mitigations will have less time to mature in development branches before release.
Current Support Structure
Bitcoin Core maintains three major release lines: versions 29.x, 30.x, and 31.x. The October 18 snapshot found 3,243 peers on 31.x, 712 on 30.x, and 635 on 29.x. Once version 32.0 releases formally, version 29.x exits the maintenance window.
If the peer distribution remained stable, 51.1% of surveyed nodes would then run unsupported versions. The measurement excludes Tor-only nodes, non-listening nodes, and privately operated infrastructure run by exchanges, custodians, and miners.
Upgrade Challenges
Node operators face practical obstacles to upgrading. Bitcoin Core 32 changes the default format for partially signed transactions, and a user reported in October that files generated by the new graphical wallet failed to import in older Core co-signers in multisignature setups. Organizations coordinating multiple signers have reason to test carefully before upgrading.
One recent example illustrates the stakes: CVE-2024-52911, a high-severity use-after-free vulnerability in block validation, affected versions after 0.14.0 and before 29.0. A crafted invalid block could crash a node, though exploitation required mining a block with sufficient proof of work. Developers received the report in November 2024, fixed it in April 2025, and disclosed it on May 5, 2026—approximately 388 days later.
The Next Phase
Faster patches protect nodes only after operators install them. The real test will come as Bitcoin Core 32.0 ships and network adoption metrics show whether operators move to maintained versions.