Bitcoin's exposure to quantum computing threats has prompted discussion among developers and security researchers about protective measures, though proposals introduce tradeoffs between security and access.
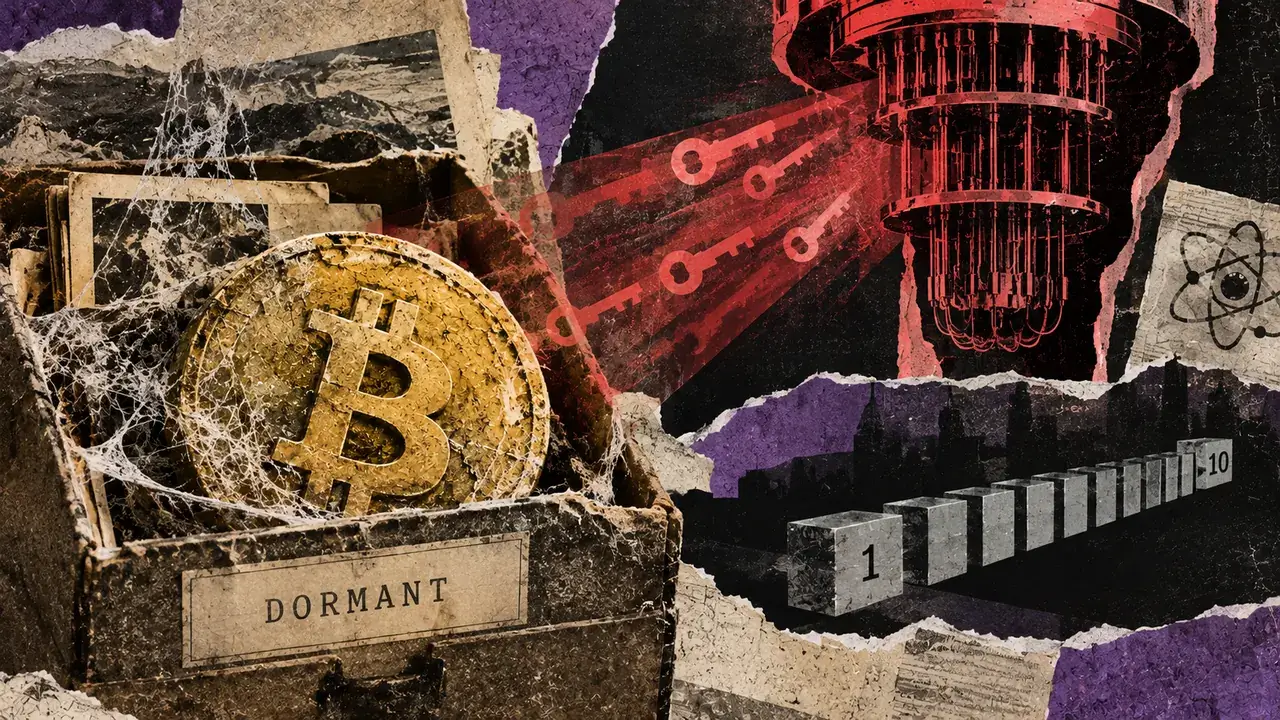
Glassnode's May 2024 analysis identified 6.04 million BTC—approximately 30.2% of then-issued supply—with publicly exposed keys. These keys remain vulnerable to potential future quantum computers capable of running Shor's algorithm to recover private keys from public addresses.
A quantum attacker with sufficient computing power could theoretically recover private keys from early pay-to-public-key outputs, enabling unauthorized spending. Crypto investor Nic Carter has outlined a scenario where recovered keys could move dormant coins across multiple blocks, potentially shaking confidence in the network.
Technical constraints and feasibility
Whether millions of Bitcoin could move simultaneously depends on blockchain capacity. Early outputs holding significant quantities could theoretically fit within 10 blocks under Bitcoin's weight rules, though actual confirmation would depend on mining decisions, competing transaction traffic, and fee dynamics.
Glassnode's exposure measure includes both actively held coins with visible keys and structurally exposed outputs such as pay-to-public-key and Taproot formats. Security researcher Jameson Lopp estimated roughly 2.6 million exposed BTC might be unable to migrate, factoring in holder inactivity and known entity labels.
Proposed solutions and tradeoffs
Several Bitcoin Improvement Proposals aim to address quantum vulnerability. BIP-360 proposes a new output type without exposed key spending paths. BIP-361 suggests phased restrictions on vulnerable destinations beginning approximately three years after activation, with tighter legacy-signature spending rules to follow roughly two years later.
Alternative approaches include Dan Robinson's PACT concept, which explores private timestamps to prove address control, and the Hourglass V2 draft, which would throttle spending from vulnerable outputs.
These proposals present distinct challenges. Restricting legacy signatures protects future security but risks locking out owners unable to migrate to new formats or meet rescue conditions. Owners without access to ownership-proof mechanisms—particularly bare pay-to-public-key holders—face unresolved recovery options.
Google has set a 2029 target for precautionary cryptographic migration, providing a reference timeline for potential quantum threats.
These remain research concepts and proposals under Bitcoin's development process, subject to community evaluation and adoption through software and ecosystem acceptance.