Attackers compromised Bitget exchange systems through a zero-day vulnerability on August 31, according to a Slowmist investigation released today. The intruders maintained access for 25 days before stealing approximately $388 million from the exchange's hot wallets on September 24.
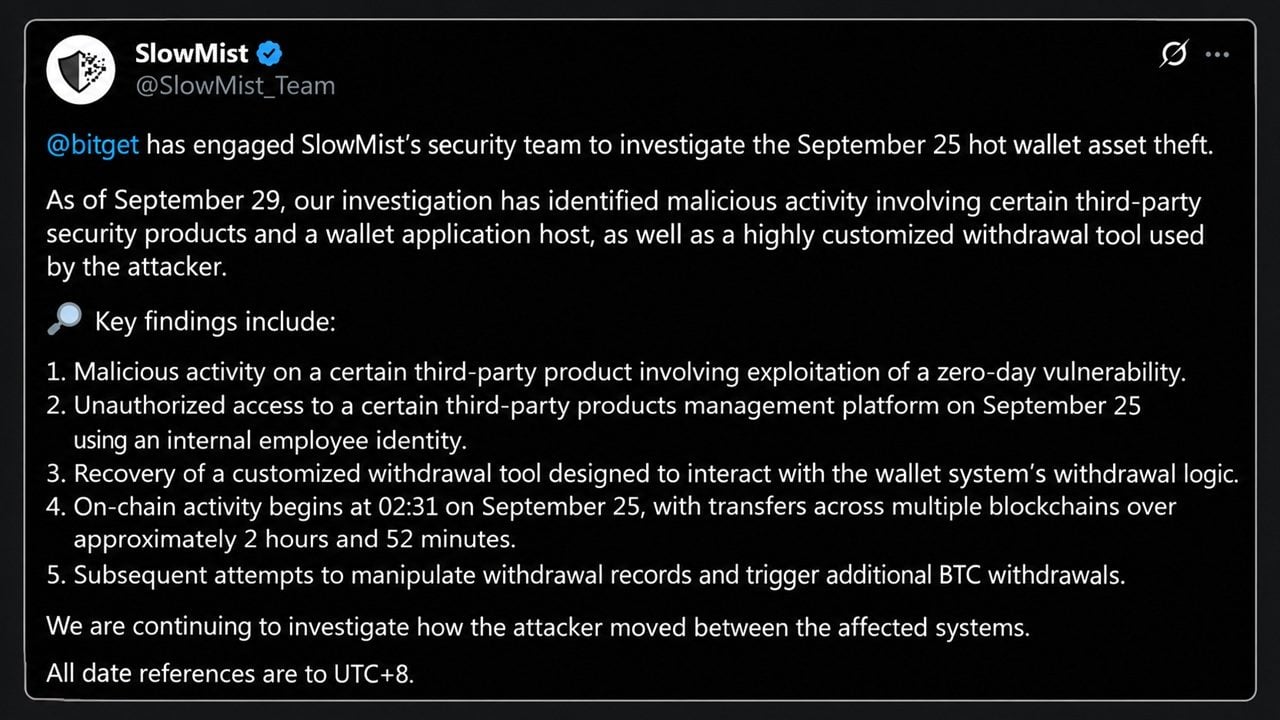
Bitget engaged Slowmist, a blockchain security firm, on September 25 to investigate the theft. The investigation found that malicious activity first appeared in logs dated August 31, when a third-party security product—referred to as "Product A" by Slowmist—was compromised through an unknown software flaw. The attacker executed a hidden script that accessed a database password and connected to the system. Similar activity appeared on two additional nodes on September 23 and September 25.
The Theft Sequence
On September 24, the attacker used stolen employee credentials to access an internal management platform from a second vendor tool, referred to as "Product B." The sequence of events, logged in UTC+8, proceeded as follows:
- A hidden script injected system commands into the management platform
- A customized withdrawal tool began executing transfers, forging risk-control parameters and triggering the withdrawal process
- The first onchain transfer occurred at 18:31 UTC, followed by additional transfers over approximately 2 hours and 52 minutes
According to Arkham Intelligence, $228 million left the exchange in just 18 minutes across seven blockchains, with XRP comprising approximately $153 million of that amount. The attacker also attempted to rewrite withdrawal records in the wallet database, though some fabricated orders returned errors. No private keys were stolen; instead, attackers manipulated the internal approval system to authorize transfers that appeared legitimate.
Fund Movement and Laundering Attempts
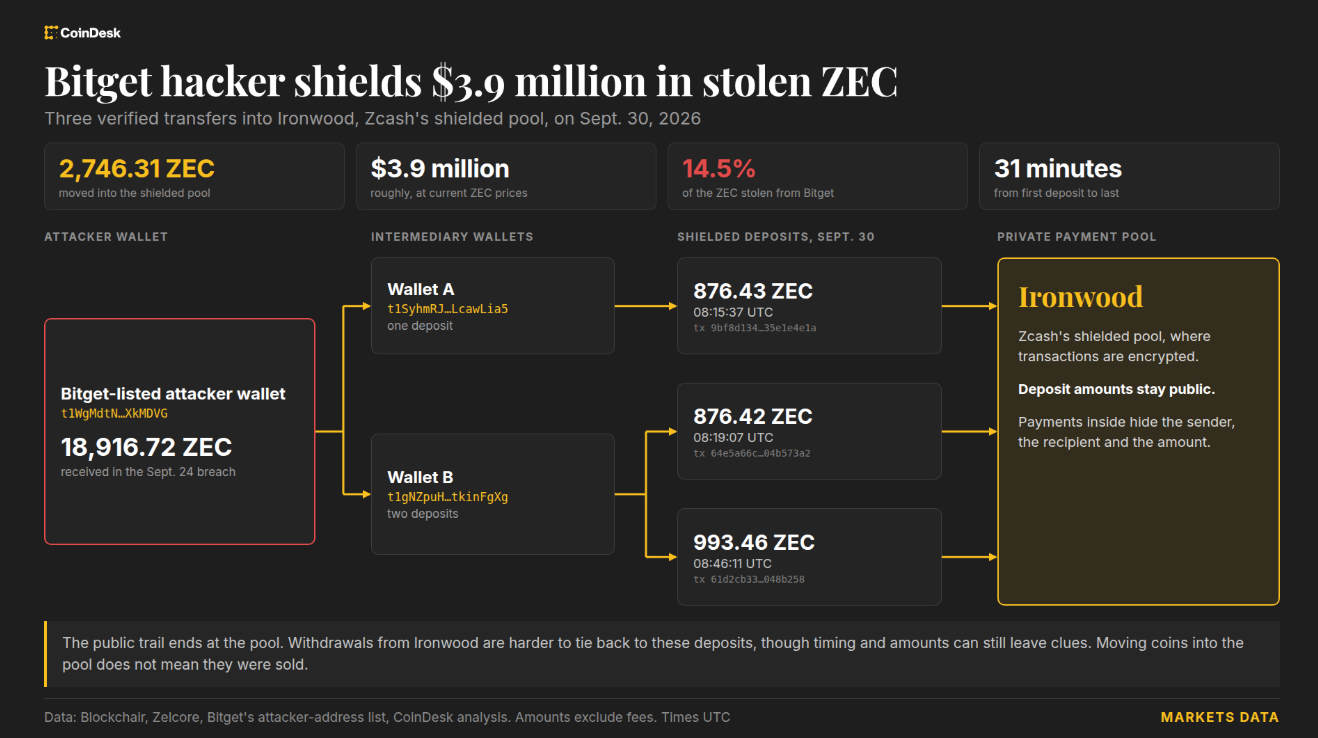
Following the theft, suspected North Korean hackers have been routing stolen funds through multiple protocols. Mistrack identified activity combining CoW Protocol, a decentralized exchange aggregator, with Chainflip to convert assets into bitcoin. Automated scripts place swap orders on CoW Protocol with recipients set to Chainflip deposit contracts, allowing assets to flow into cross-chain swaps.
Other protocols have blocked or limited laundering attempts. Near Intents blocked most of a $50 million laundering attempt, allowing $166,000 through while freezing $503,000. Earlier flows used Thorchain, Uniswap, 1inch Fusion, and Stargate.
User Compensation and Broader Security Concerns
Bitget stated its User Protection Fund, holding more than $464 million, will cover losses. The exchange is returning withdrawals in stages, beginning with bitcoin followed by ether, USDT, and other assets.
Slowmist did not identify the vendors behind the compromised security products and stated it is still investigating how the attacker moved between systems. Security experts warn that any exchange using the same security infrastructure should review logs dating back to the end of August to identify potential compromise.