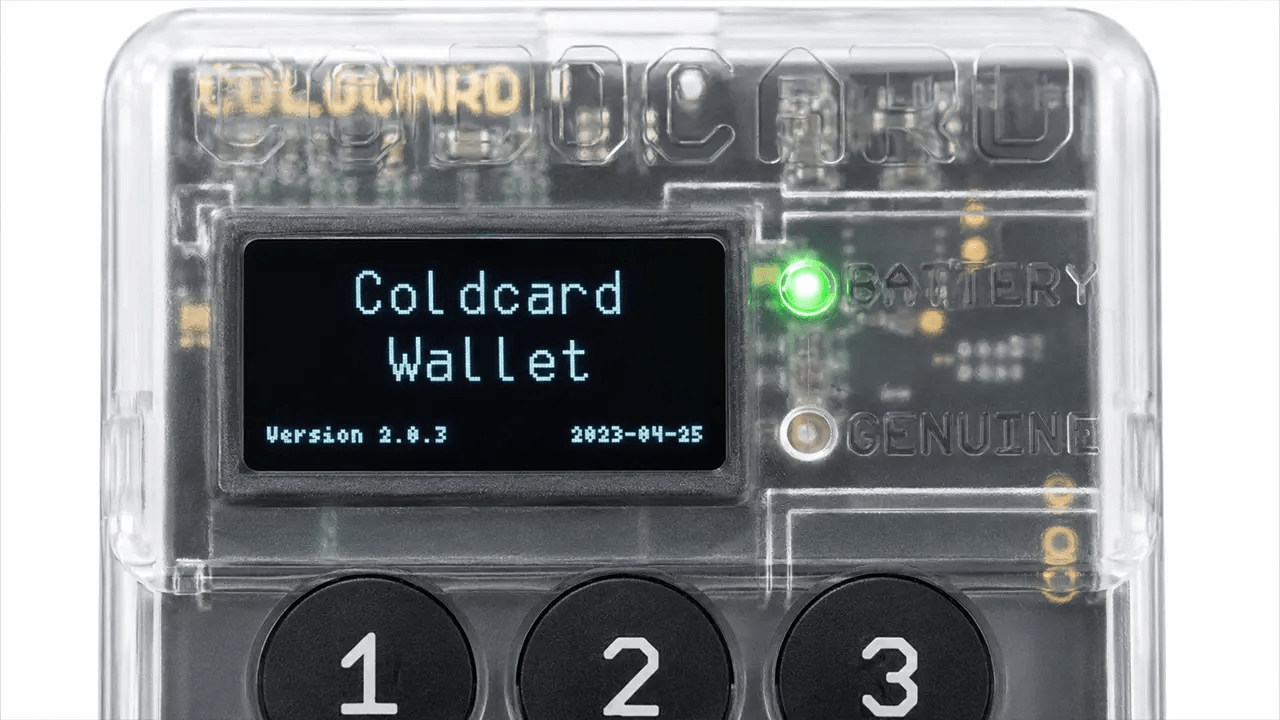
Coldcard is facing renewed security scrutiny after a fraudulent post appeared on its official X account on October 11. The message warned customers about a supposed critical seed-generation vulnerability and directed them to a phishing website.
The post was deleted within hours. Coldcard stated that its account credentials and offline two-factor authentication remained secure, and the company's internal investigation found no evidence of unauthorized login or session activity.
How the Phishing Attack Unfolded
The fraudulent message appeared around 2 a.m. UTC and presented itself as an urgent security update. It referenced several Coldcard hardware models and instructed users to migrate their wallets immediately to a deceptive website using Coldcard's name.
Community members quickly identified the suspicious post. Around 5:46 a.m. UTC, Coldcard acknowledged the incident and warned customers against interacting with the malicious link. The company emphasized that coldcard.com is its only official website.
Coldcard subsequently requested an urgent investigation from X Support, raising questions about possible platform-level or administrative access vulnerabilities. The company acknowledged reports of X administrative credentials being offered on darknet markets but stated that no connection to its incident had been established.
Context: July's Major Firmware Failure
The timing of the phishing attempt compounds Coldcard's credibility challenges. In July, the company disclosed a serious firmware defect involving defective seed generation that reportedly dated to March 2021. The vulnerability reportedly allowed attackers to reconstruct wallet seeds offline.
Coldcard estimated that 1,600 to 1,800 bitcoin were stolen, valued at approximately $100 million to $130 million at the time. The company subsequently issued firmware fixes and instructed affected customers to migrate their funds.
Sunday's phishing post exploited precisely that concern, using language of legitimate security guidance to direct users to a malicious website.
Growing Customer Frustration
The phishing incident follows a contentious October 9 social media post in which Coldcard promoted transparent hardware cases as protection against physical tampering. Critics argued that the timing was inappropriate and that transparent cases offered no protection against the software defects responsible for July's losses.
Several members of the crypto community characterized the post as tone-deaf, and some customers and observers have accused Coldcard of blocking critics on X.
No confirmed financial losses have been attributed specifically to the October 11 phishing attempt. Coldcard continues to direct customers to its legitimate website for firmware updates and security information.