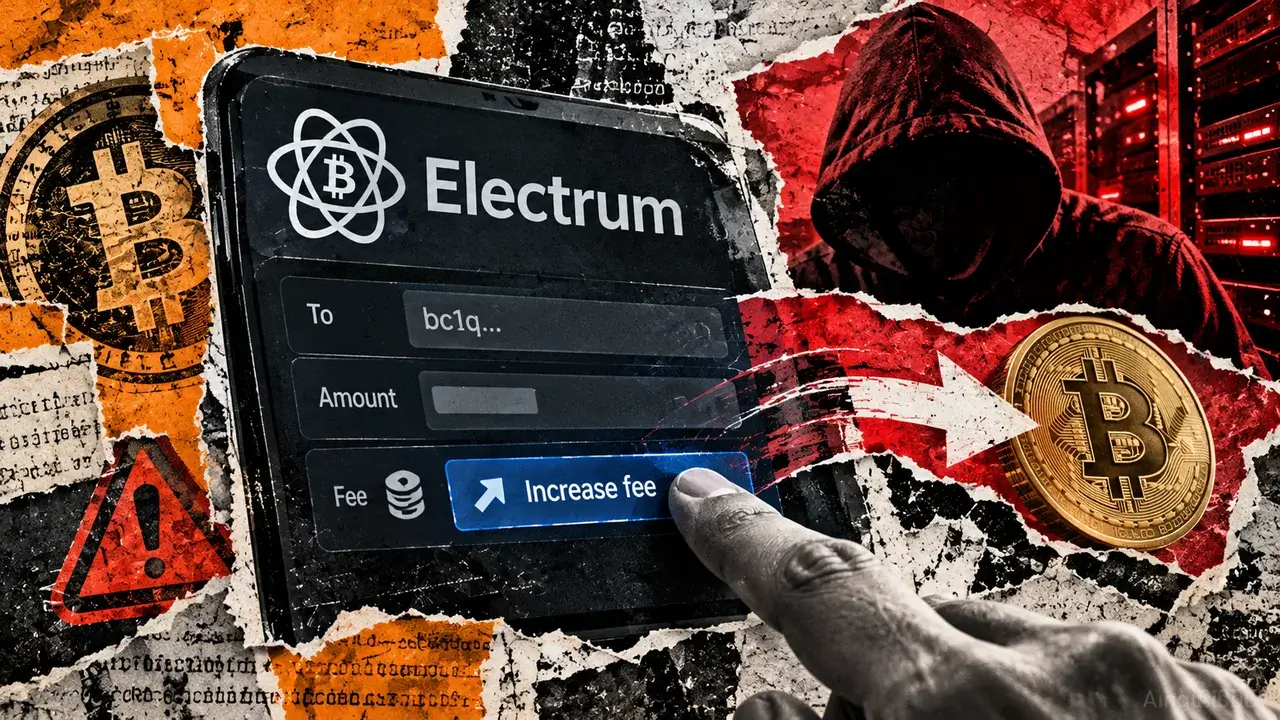
Bitcoin wallet Electrum has patched a high-severity security vulnerability that allowed hackers to redirect payments when users attempted to increase transaction fees. The developers disclosed the flaw on October 24, confirming that malicious servers had actively exploited the weakness and that at least one user lost Bitcoin after unknowingly approving a fraudulent transaction.
The vulnerability affected Electrum versions earlier than 4.8.3 and exploited the wallet's reliance on external servers to track unconfirmed transactions. Attackers could manipulate the payment information users saw before authorizing additional fees, potentially deceiving them during the fee-adjustment process.
How the Attack Worked
When a user broadcast a Bitcoin payment, a malicious server could withhold the transaction from the network and supply a conflicting version that redirected funds to an attacker-controlled address. The fraudulent transaction initially contained invalid signatures, making it unable to process as a legitimate payment. However, affected Electrum clients failed to verify those signatures before displaying the substituted transaction in the wallet's unconfirmed history.
Attackers generated Bitcoin addresses matching the final four characters of intended recipients' addresses, potentially deceiving users who relied on partial address verification. When users manually increased fees on the substituted transaction using Bitcoin's Replace-by-Fee feature, Electrum generated fresh signatures authorizing the altered payment details, making the attacker-directed transaction valid without compromising the user's private keys.
Two incidents prompted the disclosure. The first user, reporting on October 11, noticed an unfamiliar transaction appearing in their wallet after broadcasting a payment. A second user, reporting on October 18, lost funds after attempting to accelerate a pending transfer. In the second incident, attackers reportedly set the fraudulent transaction fee to zero, potentially encouraging the victim to raise it. Electrum did not disclose the total amount stolen or the number of compromised wallets.
The Patch and Recommendations
Electrum's latest release introduces signature verification for wallet-owned inputs before unconfirmed transactions enter the client's local history, preventing the substitution technique from reaching the fee-adjustment stage. The developers tagged version 4.8.3 on October 23 and distributed the updated software on October 24.
The developers advised users to download the patch from Electrum's official website and verify complete recipient addresses and payment amounts whenever signing transactions. Clients connected exclusively to trusted servers, including privately operated ones, are not exposed to this attack. The patch does not extend signature verification to every incoming transaction.