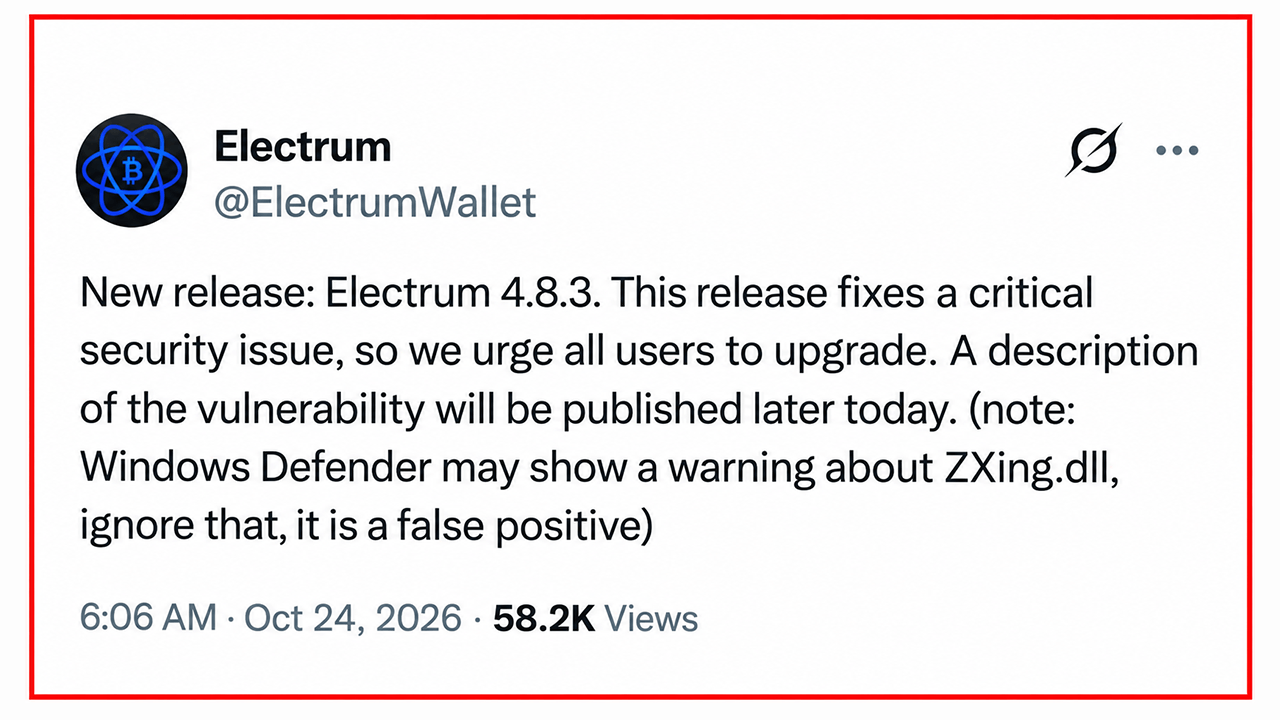
Electrum released version 4.8.3 on Saturday to address a high-severity vulnerability that allowed malicious servers to substitute legitimate Bitcoin transactions with fraudulent ones. The flaw, documented in GitHub advisory GHSA-6jp4-8v48-cc5v, affected all earlier versions of the lightweight wallet.
How the Attack Worked
Electrum relies on external servers for transaction histories, fee estimates, and payment broadcasting. While the wallet independently verifies confirmed transactions, earlier versions accepted certain unconfirmed transactions without verifying their cryptographic signatures.
A compromised server could intercept a legitimate payment, prevent its broadcast, and substitute a fraudulent transaction directing funds to an attacker-controlled address. Although the replacement carried invalid signatures, Electrum displayed it as an ordinary pending transaction.
The attack became particularly effective when users attempted to increase transaction fees using Replace-By-Fee (RBF). Instead of increasing the fee on their original payment, victims could inadvertently sign the substituted transaction, authorizing the transfer of their own bitcoin to the attacker.
Attackers further obscured the swap by generating receiving addresses whose final four characters matched the intended destination, making quick address verification less likely to expose the substitution. Some fraudulent transactions carried zero fees, apparently designed to encourage the fee adjustment needed to complete the theft.
Real-World Exploitation
Electrum developers received two private security reports. On October 11, a user reported transaction substitution, though the fee-bump mechanism wasn't fully understood at that time. On October 18, another report confirmed actual fund loss following a fee increase approval, establishing that the attack was not merely theoretical.
The Fix and User Recommendations
The patch, introduced through commit 90fe308, requires Electrum to verify signatures for unconfirmed transactions spending wallet coins. Fraudulent transactions with invalid signatures are now rejected before entering the wallet's local history.
Users running versions earlier than 4.8.3 should download the update exclusively from electrum.org and verify its cryptographic signatures. Until upgrading, users should carefully inspect every destination address and payment amount before signing, including during fee adjustments.
Those connecting exclusively to trusted, self-hosted Electrum servers are not exposed to this particular server-based attack.