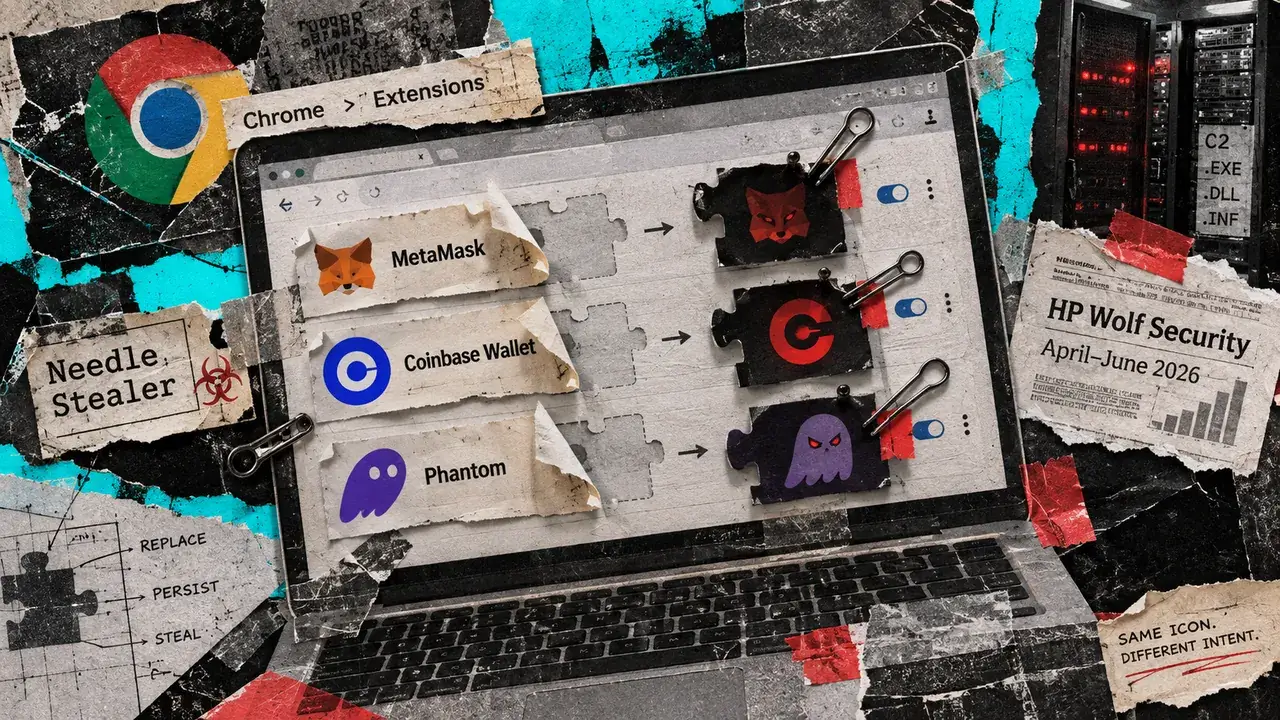
Cybercriminals have deployed malware disguised as an artificial intelligence-powered crypto trading agent to steal passwords from browser-based cryptocurrency wallets. The campaign targeted seven wallet extensions, including MetaMask, Coinbase Wallet, and Phantom, according to a security report released by HP on September 17.
The attackers created a website promoting software that claimed to use artificial intelligence to automate cryptocurrency trading. Users who downloaded the advertised trading agent instead received malware known as Needle Stealer. The operation was active between April and June, with attackers specifically targeting individuals searching online for AI tools to automate crypto trades.
Once installed, the malware identified wallet extensions on the victim's browser, then removed the genuine extension and replaced it with a malicious copy. The fake wallet appeared identical to the legitimate version, but when users entered their passwords, the fraudulent extension transmitted the credentials to a server controlled by the attackers. This stolen information, combined with wallet identification data, could grant criminals access to victims' cryptocurrency holdings.
The attackers enhanced the legitimacy of their scheme by including actual Microsoft-signed software in the installation package. This allowed the download to pass initial Windows security checks. The trusted program then executed a malicious file bundled with it, enabling the wallet-stealing software to run in the background without detection.
HP advised users to avoid entering wallet passwords or making payments through AI applications that cannot be independently verified.