Reports of Ledger hardware wallets fitted with physical spyware have emerged beyond Southeast Asia, with cases now documented across Europe and South America.
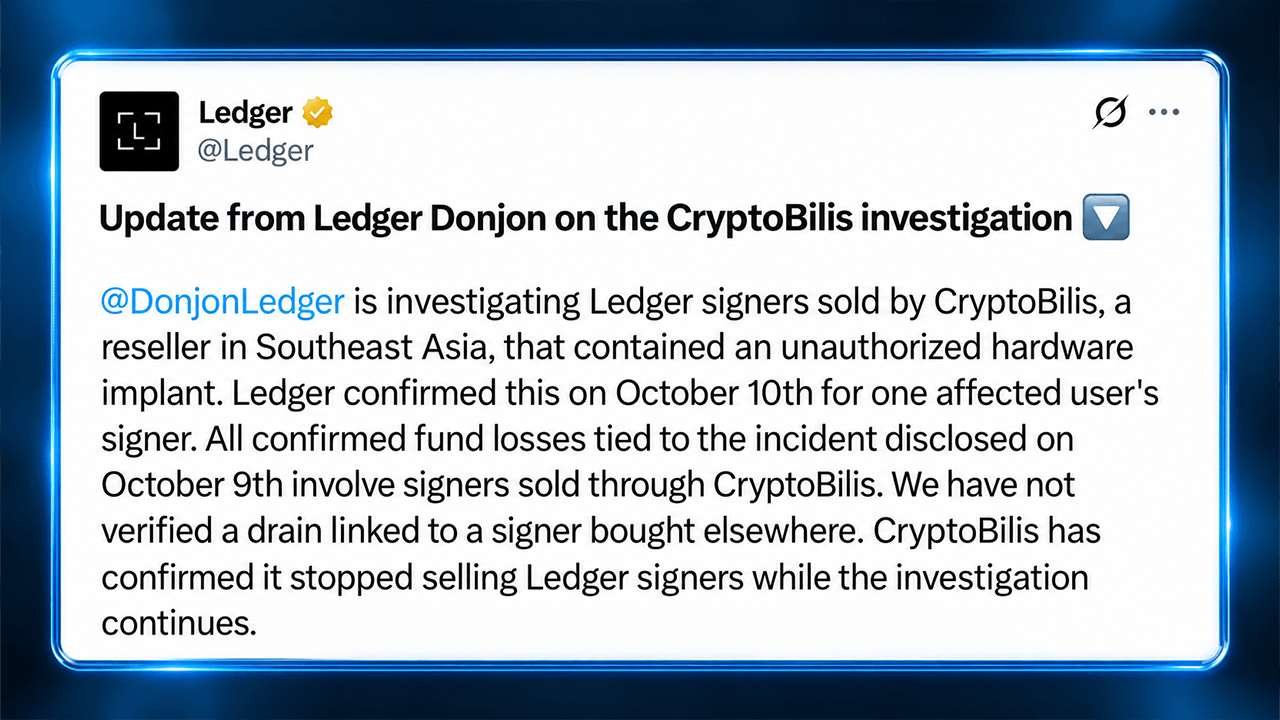
Last week, users who purchased Ledger devices from Malaysia-based reseller CryptoBilis lost over $86 million. Ledger confirmed on October 9 that a "limited" number of devices sold by CryptoBilis were affected by the tampering.
Former Mt. Gox CEO Mark Karpelès identified spyware implanted in some devices designed to read screen output and record seed phrases while evading Ledger's Genuine Check security protocol.
Additional cases identified
An X user claiming to be a semi-professional airdrop farmer reported unpacking a Ledger device with a spy implant purchased from MediaMarkt, an official Ledger reseller in Germany. The user noted similar cases had been reported in Asia, South America, and Europe.
Another user shared images of a Ledger wallet purchased from LazMall, an official Philippine reseller, which Karpelès identified as containing an earlier style of spyware. Karpelès also helped identify spyware in a Ledger Stax model purchased from CryptoBilis.
However, dozens of users who dismantled their devices out of caution were told by Karpelès that their wallets were clean.
Ledger's response
Ledger urged authorized resellers and distributors to source products only through authorized channels and to avoid restocking returned products.
CryptoBilis' former CEO revealed that the firm was acquired earlier this year and that he has stepped down from operations. He stated the company's social media account is now under new management.