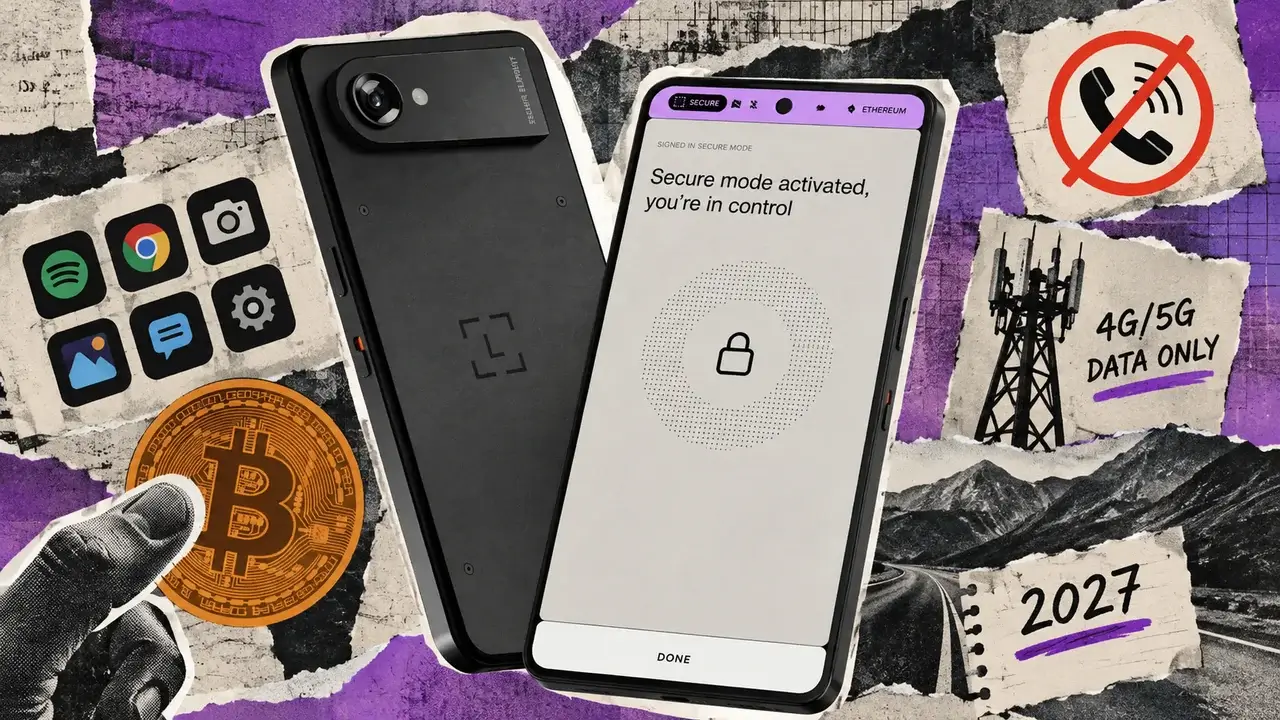
Ledger unveiled Ledger Atom on October 15, an $849 mobile device combining everyday applications with hardware-protected cryptocurrency transactions. The company is accepting refundable $100 deposits for a Founders Edition, with deliveries targeted for 2027.
The launch coincides with Ledger's investigation into an organized criminal operation that secretly modified genuine hardware wallets before returning them to reseller distribution channels. Attackers allegedly captured customers' recovery phrases and used them to drain cryptocurrency holdings in a coordinated operation.
Enhanced Security Features
Ledger's Chief Technology Officer Charles Guillemet stated that Atom includes an active protective shield designed to detect attempts to physically open, probe, or modify the device's secure hardware. The technology addresses a vulnerability exposed by recent attacks, where malicious components intercepted information displayed during wallet setup.
Existing Ledger devices use cryptographic authentication to verify the integrity of their secure software, but cannot detect additional components secretly monitoring the screen. Atom's protective shield alerts its Secure Element when the protected hardware is disturbed, potentially detecting manipulation before a compromised device reaches a customer.
The device combines an Android-based environment for everyday apps with a separate Ledger operating system that controls private keys and approves transactions. During sensitive operations, the secure processor takes control of the display, preventing ordinary applications from interfering with the approval process. Users can physically disconnect cameras and microphones through a dedicated privacy switch.
Atom supports 4G and 5G connections but lacks conventional cellular calling and SMS capabilities. Ledger partnered with Solana Mobile to preload the Seeker application, giving Atom users access to the Solana decentralized application ecosystem.
Investigation Into Distribution Compromise
On October 15, Ledger reported that criminals spent months purchasing genuine devices, installing custom-built components, and returning modified products to distribution through Southeast Asian resellers. The operation involved dedicated infrastructure to collect stolen recovery phrases, transfer cryptocurrency, and launder proceeds, with attackers investing millions of dollars in preparation.
Ledger maintained that its internal systems, chips, and operating software remained secure, attributing the attacks to device manipulation after products left its control. The company asked authorized resellers and distributors across Southeast Asia and Hong Kong to suspend sales and examined devices from stores and warehouse samples, reporting no signs of compromise among inspected units.
Unusual Victim Identified
Blockchain analytics firm Chainalysis identified an unusual victim of the thefts: an operator of a fraudulent online employment scheme who lost more than 60 Bitcoin, worth approximately $4.8 million. The operation paid participants to create artificial sales and reviews for legitimate products, showing victims negative account balances and instructing them to deposit their own money before receiving promised earnings.
The suspected operator transferred proceeds to three Ledger addresses on September 22. On October 9, the operator emptied all three wallets through individual transactions, sending the Bitcoin to a destination address identified as holding stolen funds.
Operational Changes
The security incident has prompted changes to Ledger's reseller operations. Authorized sellers have been reminded that they must never resell returned devices, regardless of apparent condition. New requirements also prohibit displaying products on store shelves, while unusual customer reports must be escalated to the company.
Ledger is working with law enforcement and blockchain security researchers to trace the attackers.