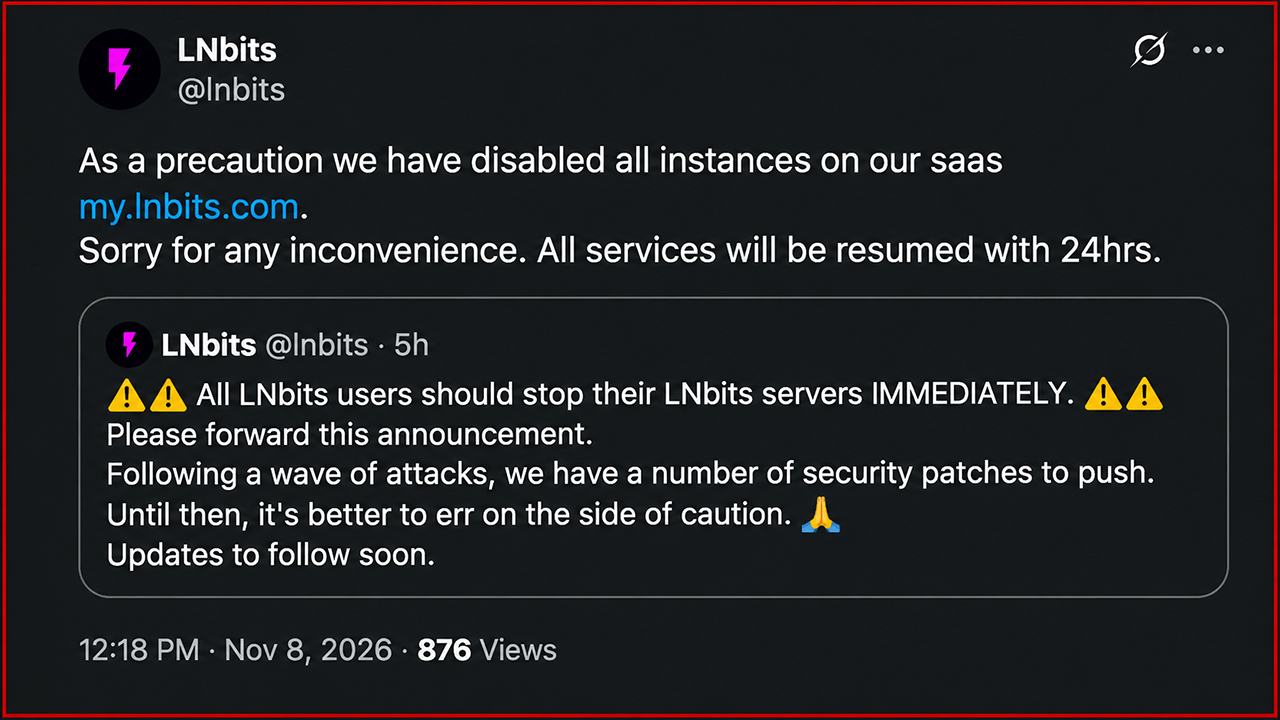
LNbits, an open-source tool for running Bitcoin Lightning Network wallets, has asked all users to shut down their servers after multiple reports that attackers were creating new accounts and withdrawing funds without authorization. The warning was issued on November 8, 2026.
What happened
According to the reports, attackers opened fresh accounts on LNbits instances and then withdrew funds they were not entitled to. One of the clearest public examples came from @KevinR4v, who runs BitTipBot. The operator reported losing approximately 2,285,545 sats, or about 0.0229 BTC.
For context, a sat is the smallest unit of Bitcoin, equal to one hundred-millionth of a single coin. Lightning users often think in sats because the network is designed for small, fast payments.
The BitTipBot attack reportedly occurred over a roughly five-hour window, starting at approximately 9:22 UTC and continuing until about 14:00 UTC. The operator has said they are committed to reimbursing affected users. However, the funds remain inaccessible until the security patches are applied, leaving users waiting on LNbits before they can be made whole.
Patch timeline
After advising users to shut down their servers, LNbits said it is working on multiple security patches and expects to release them within 24 to 48 hours of the warning. The project also asked the community to spread the advisory as widely as possible. Because LNbits is a decentralized, self-hosted tool, there is no central switch that can protect every instance; each operator must hear the warning and act individually.
This is not the first time LNbits has addressed security issues. Earlier vulnerabilities were fixed in September 2026 with the release of version 1.6.0, which followed an audit by V12.
Background: why LNbits matters
LNbits lets users manage multiple wallets and accounts within a self-hosted layer on top of the Lightning Network. Operators can build tip bots, point-of-sale setups, or shared wallets for groups without handing custody to a large company.
The timing adds context: other Lightning-related projects, including Electrum and Core Lightning, rolled out their own security updates in early November 2026. No specific link between those updates and the LNbits vulnerabilities has been confirmed.
What this means
The BitTipBot case illustrates the human cost of the downtime. Even an operator willing to reimburse users cannot do so until the software is fixed, leaving end users stuck in limbo through no fault of their own.
No immediate market reaction has been observed. The losses reported so far are small in Bitcoin terms, and the incident is centered on a self-hosted tool rather than a major exchange or custodian.
For now, the message from LNbits is blunt: turn it off, wait for the fix, and tell everyone you know who runs it to do the same.