Luxor Technology has confirmed an unauthorized redirection of bitcoin mining hashrate through its Commander platform, resolving earlier speculation about an alleged attack on thousands of mining machines. The company says the incident was contained within two hours, and affected customers will receive full compensation.
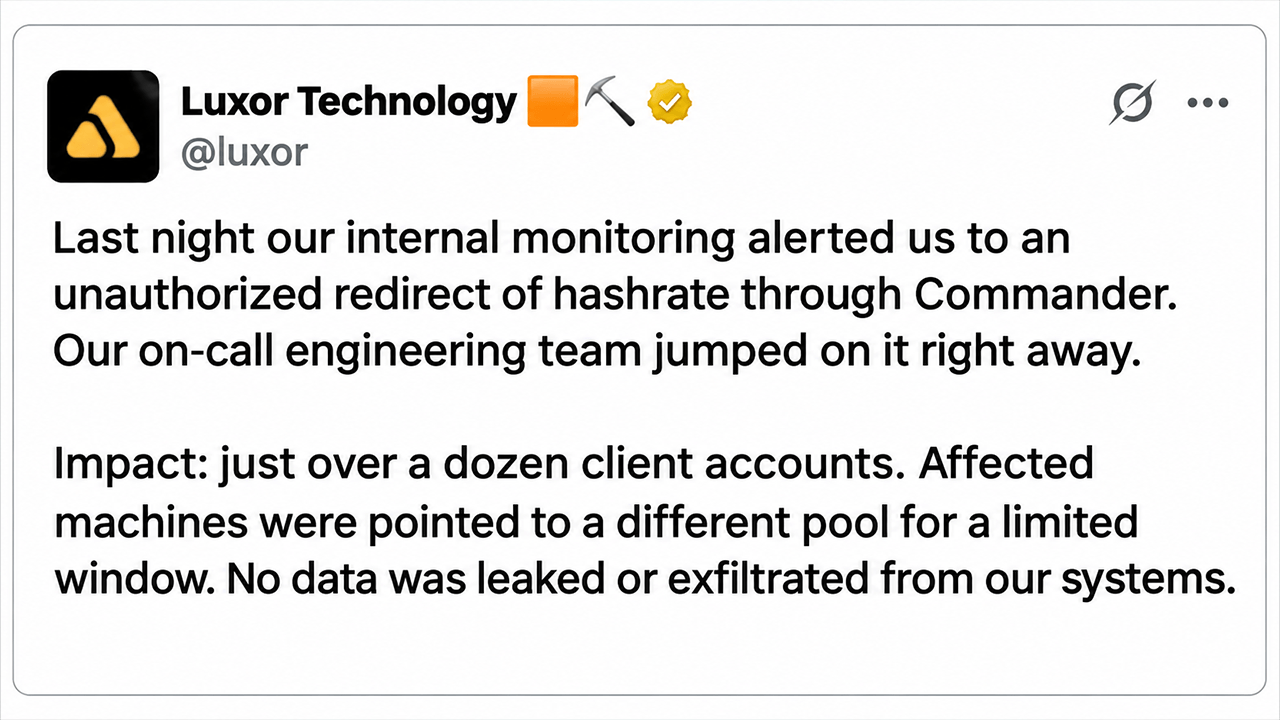
Internal monitoring systems detected unauthorized modifications to mining pool configurations on Saturday, November 14, 2026, around 6 p.m. Pacific time. Luxor's engineering team responded immediately and patched the vulnerability within two hours, restoring affected equipment to original configurations.
Scope of the Compromise
Just over a dozen customer accounts were affected by the unauthorized hashrate redirection through Commander. Mining machines were temporarily pointed to a different pool during the incident. Luxor stated that no data was leaked or exfiltrated from its systems.
Estimates indicate approximately 13 exahash per second (EH/s) was redirected to the Ocean mining pool. The compromise was confined to Commander, with Luxor's mining pool and LuxOS firmware remaining unaffected.
Compensation and Investigation
Luxor committed to reimbursing every affected customer for the computational power diverted during the incident, paying them as if the hashrate had mined normally on their intended pool.
CEO Nick Hansen attributed the compromise to what he described as a sophisticated AI-enabled vector, though Luxor has not yet published technical findings establishing precisely how attackers gained access or manipulated mining configurations. The company promised a comprehensive post-mortem examining the incident.
The incident underscores how unauthorized changes to mining fleet configurations can jeopardize revenue without requiring attackers to seize cryptocurrency directly.