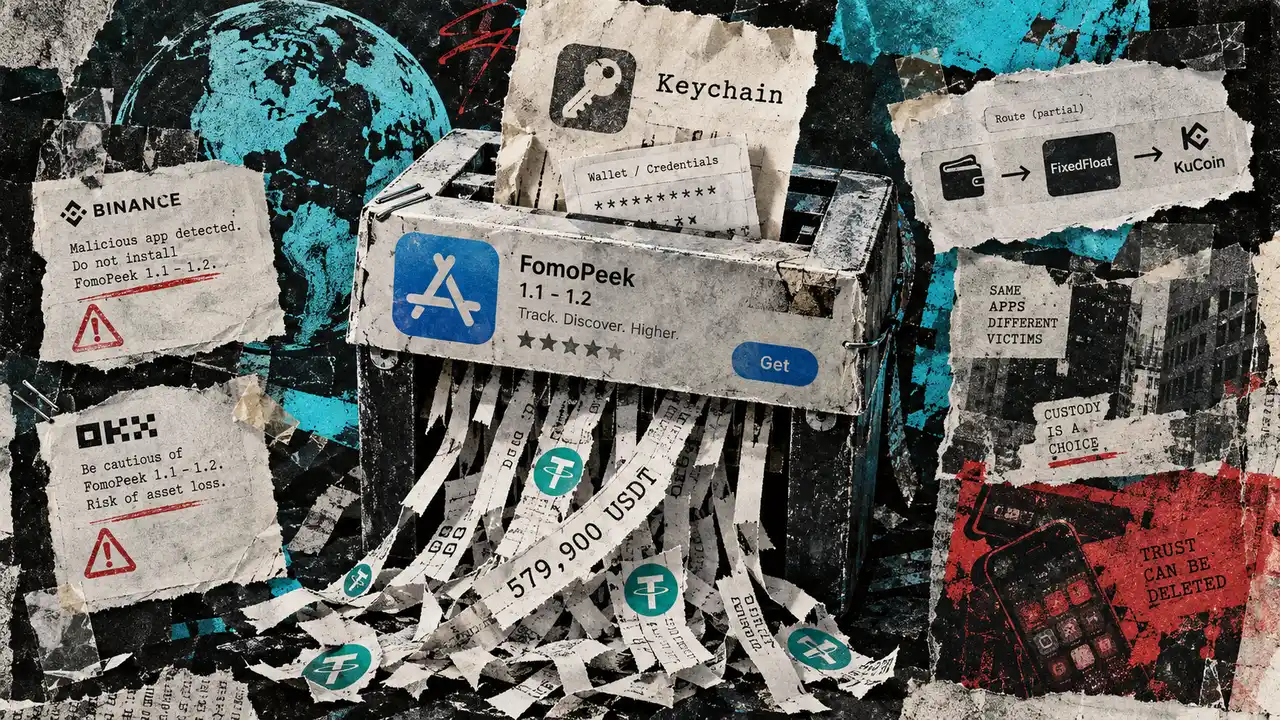
A malicious iPhone application called FomoPeek, distributed through Apple's App Store, has been linked to the theft of approximately $580,000 in USDT, according to investigations by blockchain security firm SlowMist and cryptocurrency exchange OKX.
FomoPeek was marketed as a read-only monitoring tool for tracking large cryptocurrency transactions on Ethereum, Solana, and Tron. However, versions 1.1 and 1.2 contained embedded malicious modules unrelated to its advertised functions.
Technical Vulnerability
SlowMist researchers discovered two hidden components in the compromised versions. One module communicated with external command-and-control servers, while the second contained a kernel exploitation framework with eight attack methods capable of adapting to specific iPhone models and operating-system versions.
The exploit could breach Apple's application sandbox isolation to access Keychain data—Apple's system for storing passwords and sensitive information—as well as files from other applications. This created a pathway to locally stored private keys, seed phrases, and login credentials without requiring users to enter this information into FomoPeek.
SlowMist founder Yu Xian explained that successful attacks could allow unauthorized access to system Keychain data and encrypted files from other apps, potentially exposing private keys, recovery phrases, login credentials, chat histories, and other user data stored on the device.
The malicious components first appeared in version 1.1, released September 9, and version 1.2 on September 12. SlowMist removed them in version 1.3 on September 17. The framework was also capable of receiving remote instructions that controlled whether exploitation was enabled and how frequently it would execute.
Theft and Fund Tracking
Blockchain analysis firm Salus identified address 0x6d37f2C5e8F8546b648D317295565dA95975f4BB as the attacker address and estimated proceeds at approximately 579,900 USDT. The stolen funds moved through multiple intermediary addresses and mixing services, with 401,028 USDT traced to FixedFloat, 20,000 USDT to deposit addresses at KuCoin, 111,458 USDT through an escrow platform, and 10,000 USDT through the CCE mixing service.
Salus analysis also indicated the group behind FomoPeek had been involved in a separate private-key theft in June, though investigators were still determining whether the same technique was used.
Platform Warnings and Recommendations
Multiple cryptocurrency platforms, including Binance, OKX, Gate, Bitget Wallet, and Rabby, issued warnings to users. They recommended removing FomoPeek, updating iOS, and moving assets to newly created wallets on devices where the compromised app was never installed.
Crypto firms emphasized that deleting the app or patching the operating system cannot invalidate private keys that may have already been copied by attackers. Affected users need fresh credentials generated on uncompromised devices.
Implications for Device Security
The incident highlights vulnerabilities in using dedicated iPhones for cryptocurrency security. While some have argued that isolated devices could be preferable to certain hardware wallets, the FomoPeek exploit demonstrates that even an app specifically designed for crypto users and distributed through Apple's official marketplace could breach the operating system itself, bypassing the isolation protections offered by application sandboxing.
Binance and other platforms continue monitoring for deposits of the stolen USDT to potentially restrict or track fund movement, while Salus tracks addresses linked to remaining proceeds.