Bloom Trading, a Telegram-based cryptocurrency trading bot supporting Solana and Ethereum Virtual Machine networks, experienced a significant security breach on October 26 that resulted in the loss of approximately 9,408 SOL valued at roughly $947,000.
The stolen funds were distributed across 49 wallet addresses controlled by nine users. Blockchain monitoring accounts flagged the suspicious transfers, with the largest individual drain identified as 1,636 SOL, worth approximately $166,000. Early reports indicated the attacker primarily targeted SOL holdings while leaving some USDC stablecoin balances untouched.
Vulnerability and Security Assessment
Bloom's investigation identified a complex remote code execution (RCE) vulnerability involving a third-party software module as the entry point for the attack. The company stated that no private keys were compromised and that unaffected wallets remain secure.
The distinction between an RCE exploit and direct private key extraction is significant, as such vulnerabilities can allow attackers to manipulate a compromised software environment without directly extracting users' credentials. However, Bloom has not publicly disclosed the precise mechanism used to authorize the unauthorized transfers.
Response and Reimbursement
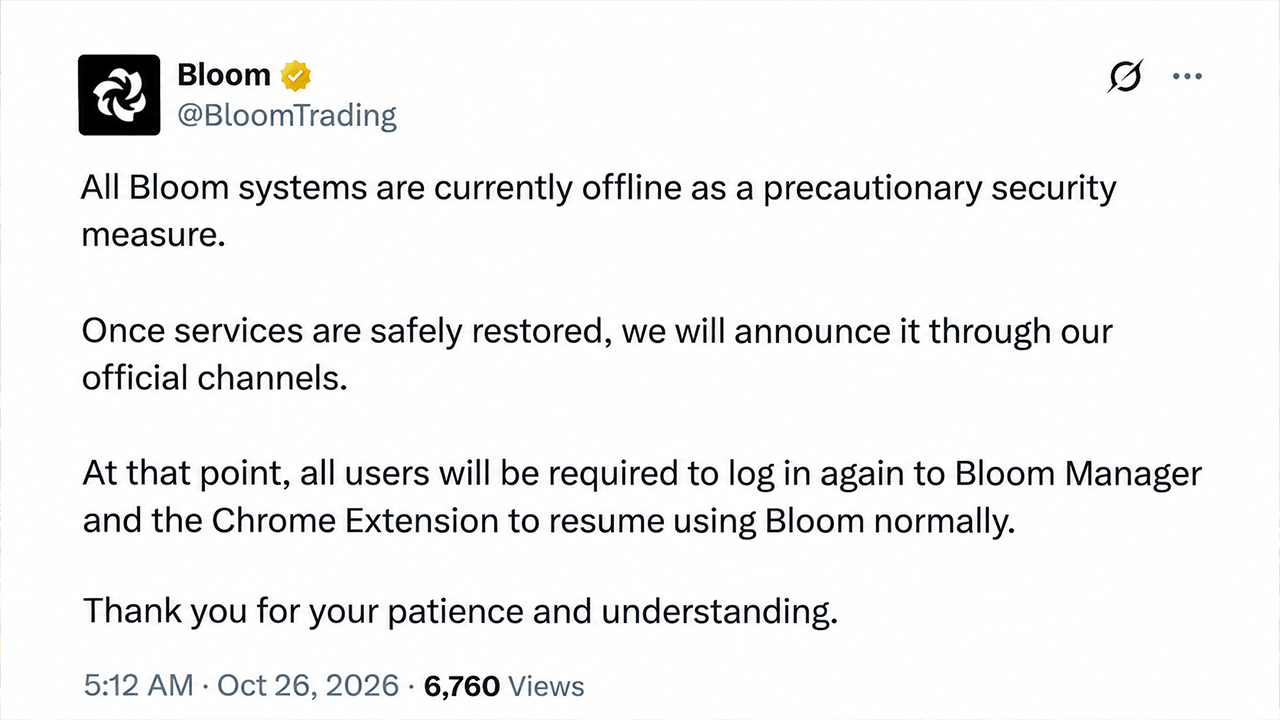
Bloom temporarily disabled services as a precautionary security measure and directed affected customers to its support channels. The company pledged to fully reimburse 100 percent of the stolen funds directly to secure wallets designated by affected users.
The company stated it is tracing the stolen cryptocurrency, exploring freezing and recovery options, and attempting to identify the attacker. Affected customers have been advised to transfer remaining assets into newly generated wallets. Bloom has not publicly established a reimbursement deadline or announced when normal operations will resume.