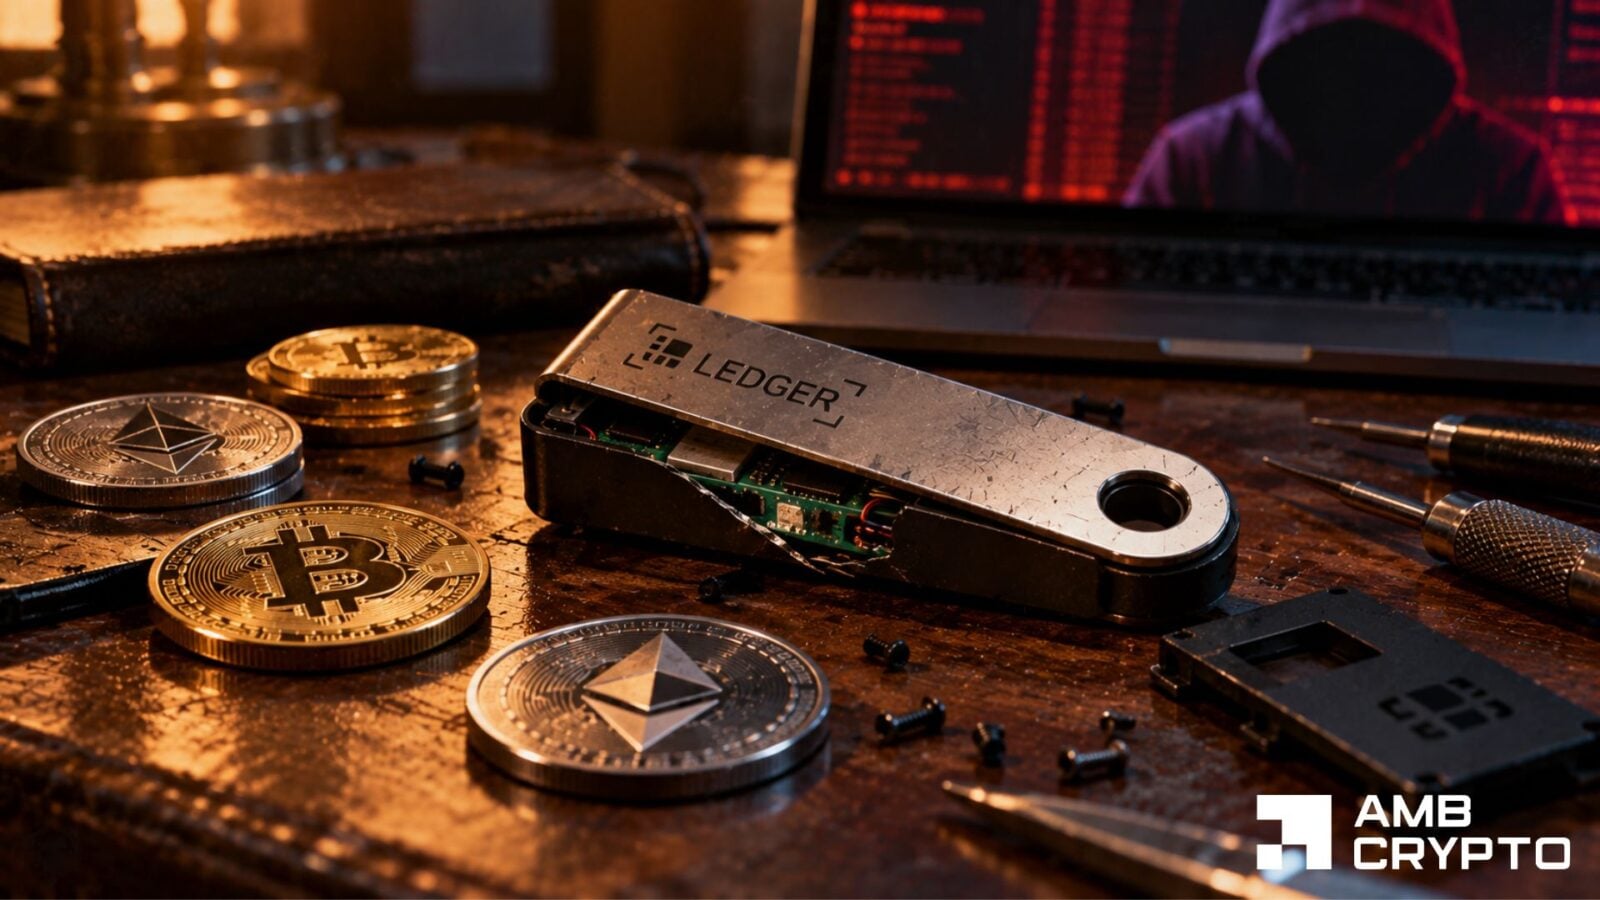

A Ledger hardware wallet purchased through a reseller contained a concealed circuit board designed to capture the device's 24-word recovery phrase, according to reports. The component was hidden behind the screen where padding should have been located and included an antenna and SIM card capable of transmitting sensitive wallet data remotely.
The discovery highlights a vulnerability in Ledger's authentication process. While Ledger's Genuine Check confirms the presence of an authentic security chip, the company acknowledges in its own guidance that this verification cannot detect all physical alterations made to the device around that chip.
The tampered wallet investigation is linked to reports of compromised accounts involving Malaysian reseller CryptoBilis. Ledger has requested the company cease selling and shipping its devices. On-chain analysis estimated losses across affected wallets at approximately $92.9 million across 311 accounts, though Ledger has not confirmed these figures.
The incident underscores a fundamental tension in hardware wallet security. These devices are designed to eliminate the need to trust third parties with cryptocurrency holdings. However, purchasing from unauthorized resellers requires trusting an intermediary with the very device that protects those assets.
Ledger officially recommends authorized resellers, including storefronts on Amazon, Shopee, and Lazada. The company has not confirmed that tampered hardware caused the reported CryptoBilis losses.