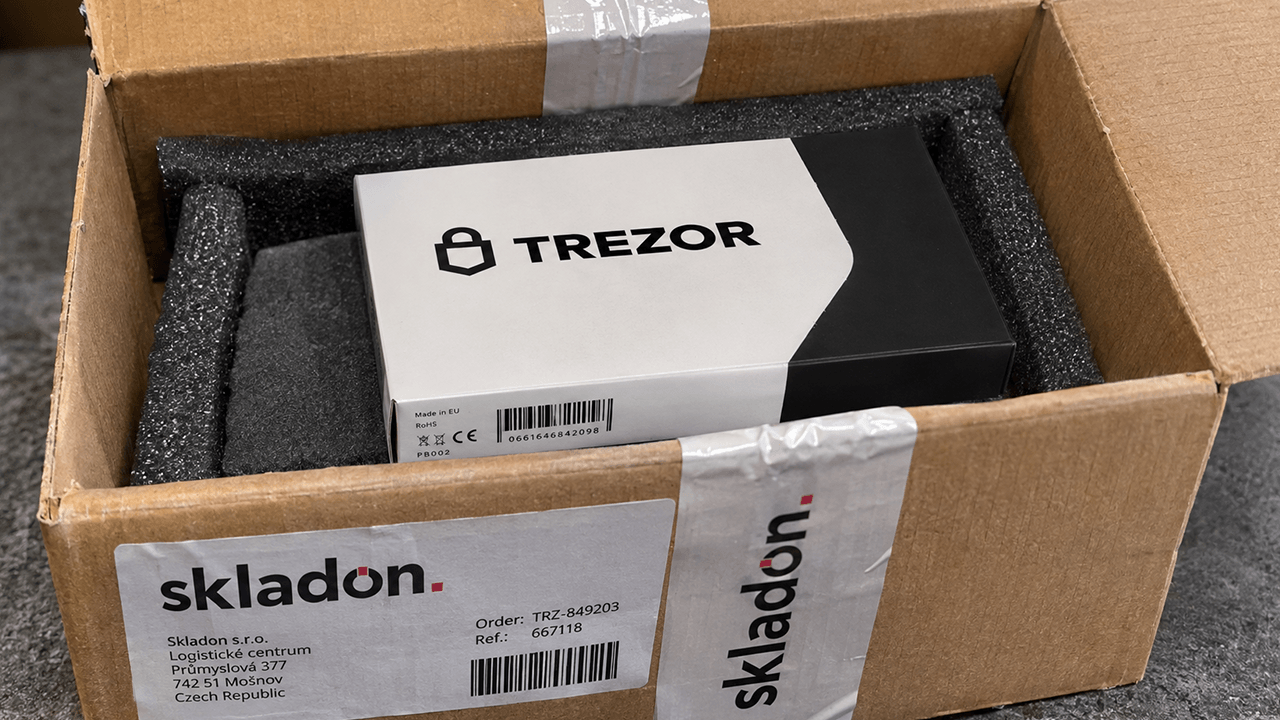
Hardware wallet manufacturer Trezor announced on November 16, 2026, that a security breach at shipping partner Skladon exposed personal information associated with approximately 27,000 customer orders. The unauthorized intrusion occurred on November 7, though Skladon did not notify Trezor until November 15.
Compromised records cover orders placed between August 9 and November 7, 2026. Exposed information includes customers' full names, telephone numbers, delivery addresses, email addresses, purchase dates, product names, and prices. The incident extends across multiple countries through Skladon's international shipping operations, though U.S. customers were unaffected.
Trezor emphasized that its wallet devices, recovery phrases, PINs, and passphrases were not compromised, as neither Trezor nor Skladon possesses that information. However, the stolen personal details present substantial privacy concerns, including potential identity phishing, fraudulent communications, and physical security threats. The company noted that some customers have already reported suspicious telephone calls following the disclosure.
Trezor advised affected customers to treat any unexpected calls, texts, emails, or letters about their orders as suspicious. The company cautioned customers to contact support exclusively through its official website and never disclose wallet backups. Those receiving credible physical threats should contact local law enforcement.
Privacy Measures Introduced
Trezor introduced several measures to strengthen customer privacy. An Anonymous Pickup service, developed since early 2026, is now available across 18 European countries. The service allows customers to purchase hardware wallets using an alias and email address, collecting orders from designated parcel lockers or pickup locations without disclosing residential addresses or telephone numbers. Germany offers a modified arrangement requiring identification, though home addresses remain unnecessary.
The company is also reducing its customer information retention period from 90 days to 45 days and requiring shipping partners to adopt equivalent standards. Trezor plans further reductions and is reviewing third-party security requirements.
This incident follows an earlier 2026 exposure involving Trezor's email provider, Brevo, which exposed newsletter addresses. Trezor has notified the relevant data protection authority and promised additional updates as investigators establish the breach's full scope.