Trezor is restructuring its authorized reseller network, with selected partners losing authorization on January 1, 2027. The decision follows a hardware implant attack discovered in Ledger devices sold through authorized channels, raising broader questions about the security of cryptocurrency wallet distribution.
In an October 13 letter, Trezor Chief Commercial Officer Danny Sanders said the company could no longer adequately inspect every partner in its existing distribution network. The company evaluated individual markets based on revenue, distribution coverage, and its ability to reach customers before deciding which partnerships to terminate.
Trezor stated it found no evidence of compromised devices within its network, describing the restructuring as a preventive measure. Sanders wrote that "a hardware wallet is only as safe as the path it travels to reach its owner."
Affected retailers will receive no additional inventory but can continue selling existing stock through the holiday shopping season. Trezor will remove them from its authorized reseller directory on January 1. The company did not disclose how many businesses would lose authorization or which markets would be affected.
Sanders acknowledged that the decision could have significant financial consequences for smaller retailers that have built their businesses around Trezor products, but stressed that the restructuring did not reflect wrongdoing by affected partners or concerns about the safety of their existing inventory.
For retailers retaining authorization, Trezor plans stricter contractual requirements and additional inspections covering how devices are sourced, stored, and handled.
Ledger Implant Attack Triggers Industry Response
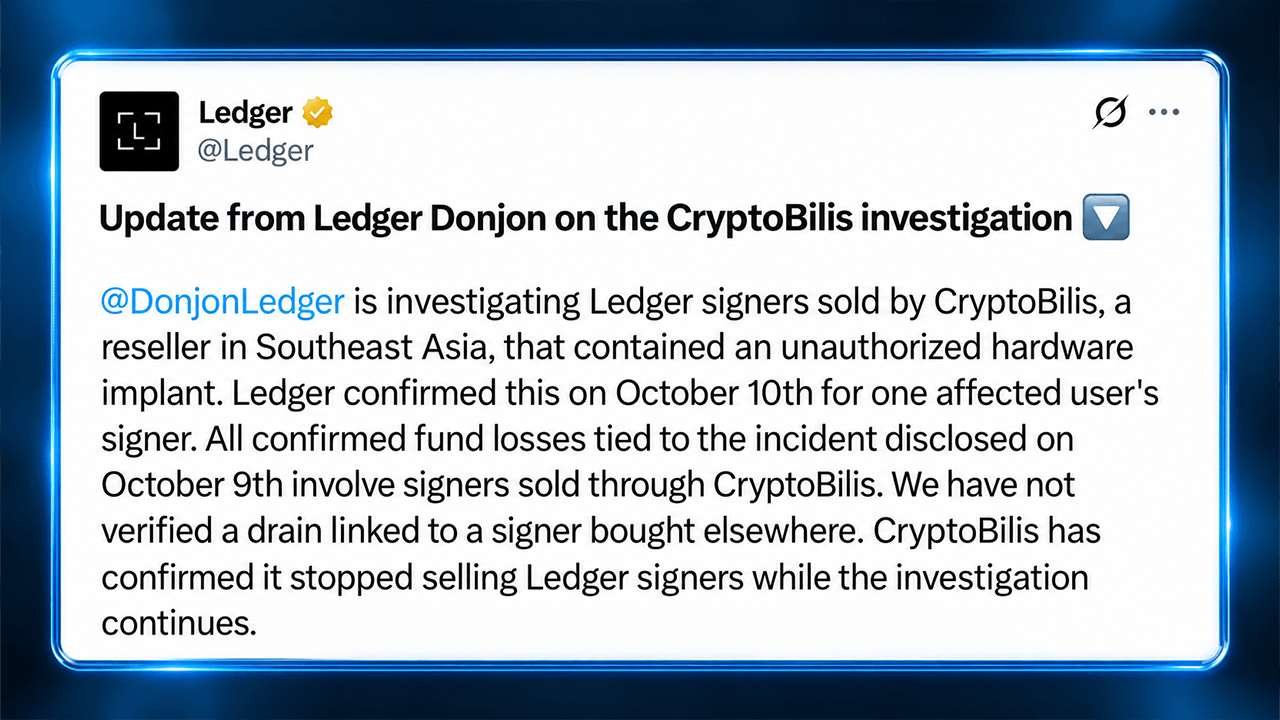
Trezor's decision follows Ledger's confirmation that attackers installed an unauthorized electronic component inside a wallet sold by CryptoBilis, an official reseller operating in Southeast Asia. The implant could capture the 24-word recovery phrase displayed during wallet setup and transmit the information through an LTE connection using an embedded eSIM.
Ledger confirmed the discovery on October 10 and said all verified thefts connected to the incident involved devices purchased through CryptoBilis, which has since stopped selling its products.
On October 13, Ledger confirmed that MediaMarktSaturn suspended sales of its hardware wallets across physical stores and online platforms following a report of an implanted device purchased in Germany. The company said it had not reported any financial losses in connection with that case.
Additional reports have emerged of implanted devices from other authorized retailers, including claims from former Mt. Gox chief executive Mark Karpelès and observations flagged by analyst Darkfost involving retailers in Singapore. These findings have not been independently confirmed by Ledger or linked to the CryptoBilis attack.
Independent blockchain investigators have linked suspected losses approaching $93 million to the broader incident, although Ledger has not verified the total value stolen or the number of affected customers. Ledger maintains that its internal systems and services remain uncompromised.