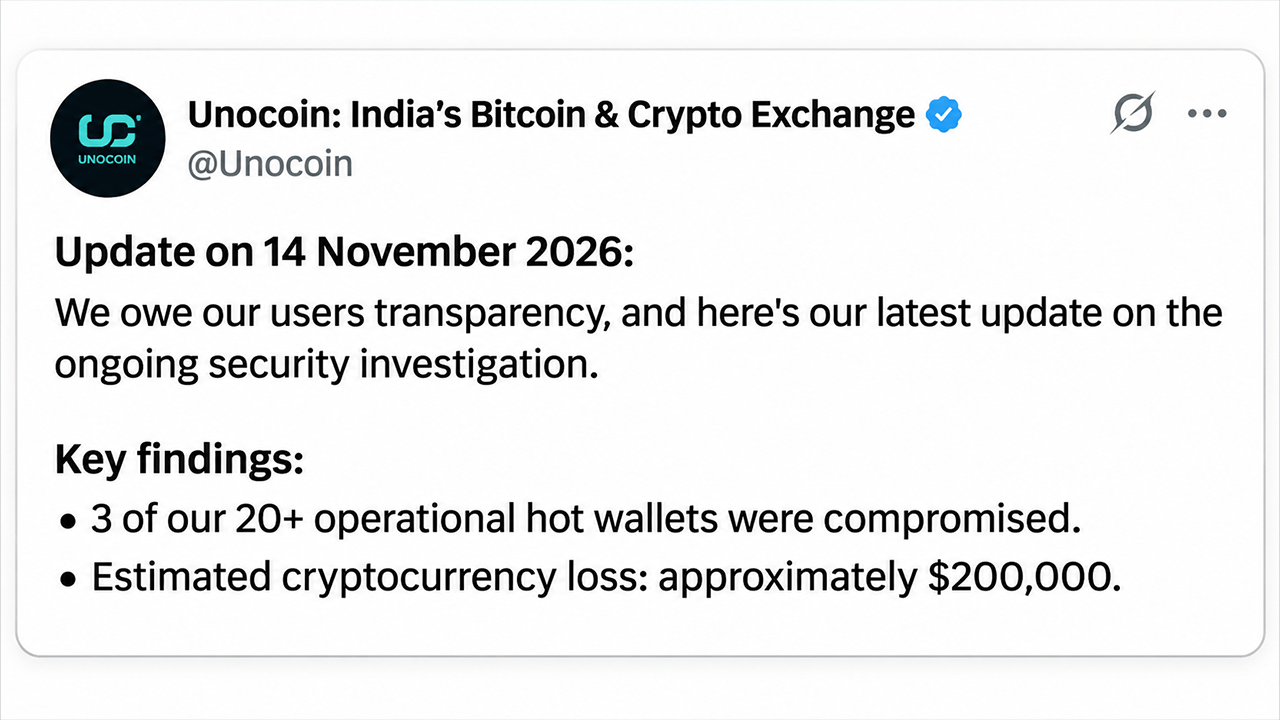
Indian cryptocurrency exchange Unocoin confirmed Saturday, November 14, that attackers stole approximately $200,000 in cryptocurrency from three of its hot wallets and potentially exposed sensitive customer information, reversing its earlier position that no funds were lost.
The disclosure marked a significant shift from Unocoin's initial assessment following a November 6 security incident. On November 9, the Bengaluru-based exchange had stated that its intervention with custody providers prevented cryptocurrency losses.
Scope of Losses and Customer Impact
Forensic examinations uncovered unauthorized transactions involving three operational hot wallets used for customer withdrawals. The estimated $200,000 loss represents significantly less than 1% of cryptocurrency assets held on behalf of customers, according to Unocoin.
The exchange pledged to absorb the financial damage and stated it would fully fund the identified loss from its own resources, ensuring that affected cryptocurrency balances would not be reduced. Unocoin also reported successfully freezing a portion of the affected funds through coordination with industry partners, though it did not disclose the amount recovered.
Backup Keys Identified as Vulnerability
Investigators determined that the breach stemmed from compromised encrypted backup signing keys generated approximately eight years ago, printed on paper, and stored in secure physical storage. These Unocoin-controlled keys were used to authorize unauthorized cryptocurrency transfers.
The exchange acknowledged that investigators have not yet established precisely how the keys were accessed, despite identifying a decryption passphrase within compromised infrastructure. Under Unocoin's two-of-three multisignature arrangement, the exchange controlled two signing keys, allowing transactions to be authorized without participation from its custody provider BitGo.
BitGo confirmed on November 13 that its custody systems were not breached and that suspicious transactions were signed using Unocoin's keys before being broadcast independently to blockchain networks.
Customer Data Exposure
Unocoin acknowledged that portions of its infrastructure may have exposed registered email addresses, residential addresses, encrypted passwords, account balances, and know-your-customer information. However, the company stated that investigators found no evidence of unauthorized access to actual identity verification documents.
Customers were warned about potential targeted phishing attempts exploiting potentially compromised personal information. Unocoin continues rebuilding its infrastructure and conducting security audits before restoring services.