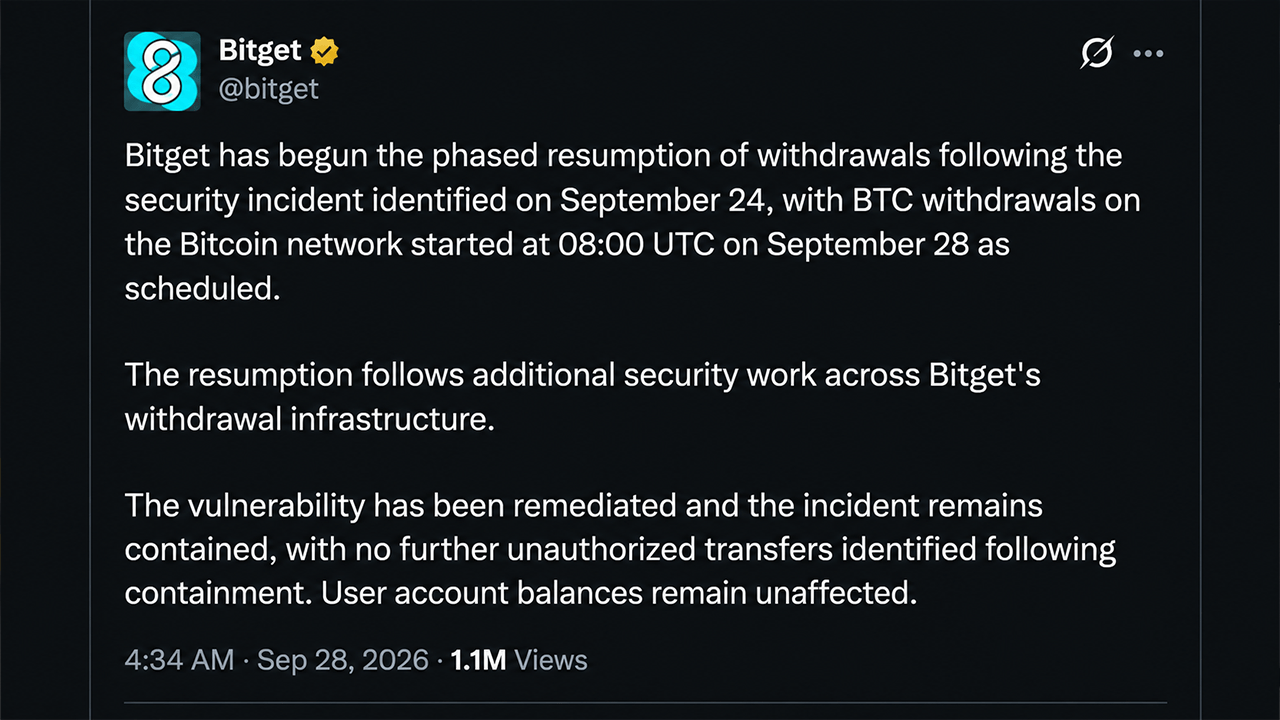
Bitget has resumed bitcoin withdrawals following a security incident on September 24 in which attackers stole approximately $388 million from the exchange. By 9 a.m. UTC on September 28, Bitget had processed 9,585 bitcoin withdrawals totaling approximately 4,098 BTC.
The exchange traced the breach to stolen credentials obtained through a vulnerability in a third-party security product. The attackers used these credentials to issue fraudulent withdrawal commands, bypassing existing risk controls. Bitget stated that private keys and cold wallets were never compromised and that customer account balances remain unaffected.
Investigation and Asset Recovery
The unauthorized transfers occurred across multiple blockchain networks, including Ethereum, XRP Ledger, and Tron, as well as platforms such as Thorchain and protocols including Uniswap, 1inch Fusion, and Stargate. Forensic specialists Mandiant and Slowmist are assisting with the investigation, and some affected assets have been frozen through coordination with industry partners.
Bitget initially estimated the loss at $351.6 million before revising the figure to approximately $388 million following reconciliation. The company clarified that the updated estimate does not represent additional unauthorized transfers after containment.
Remediation and Withdrawal Timeline
Bitget identified the attack path and remediated the vulnerability while strengthening controls across its withdrawal infrastructure. The exchange is reviewing third-party security dependencies, internal access controls, withdrawal verification, and abnormal activity detection.
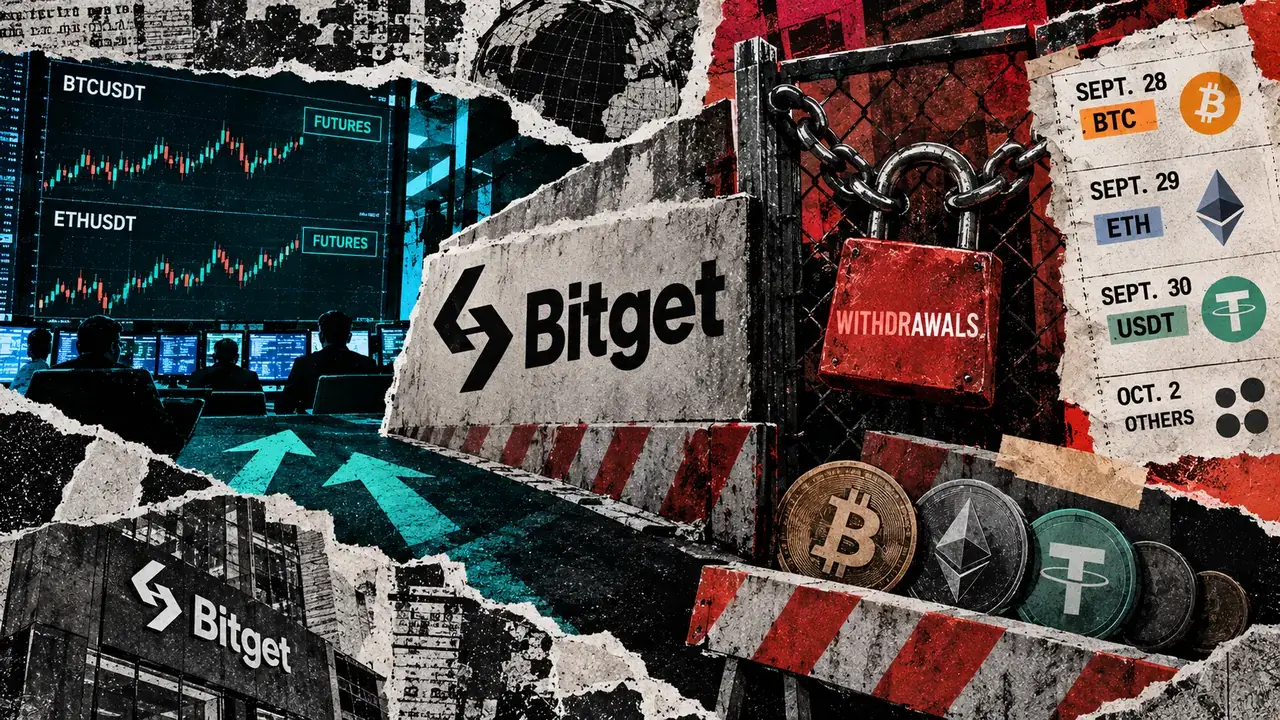
Bitcoin and BSC network withdrawals began on September 28. Ethereum withdrawals are scheduled to resume on September 29, USDT on September 30, and other supported tokens, fiat, and peer-to-peer services on October 2. Bitget expects to complete an official security report this week.
The exchange maintains a comprehensive reserve ratio of 127% and a User Protection Fund exceeding $464 million to protect customers.