A malicious iOS application distributed through Apple's App Store has been connected to approximately $580,000 in stolen cryptocurrency, according to blockchain security firm SlowMist.
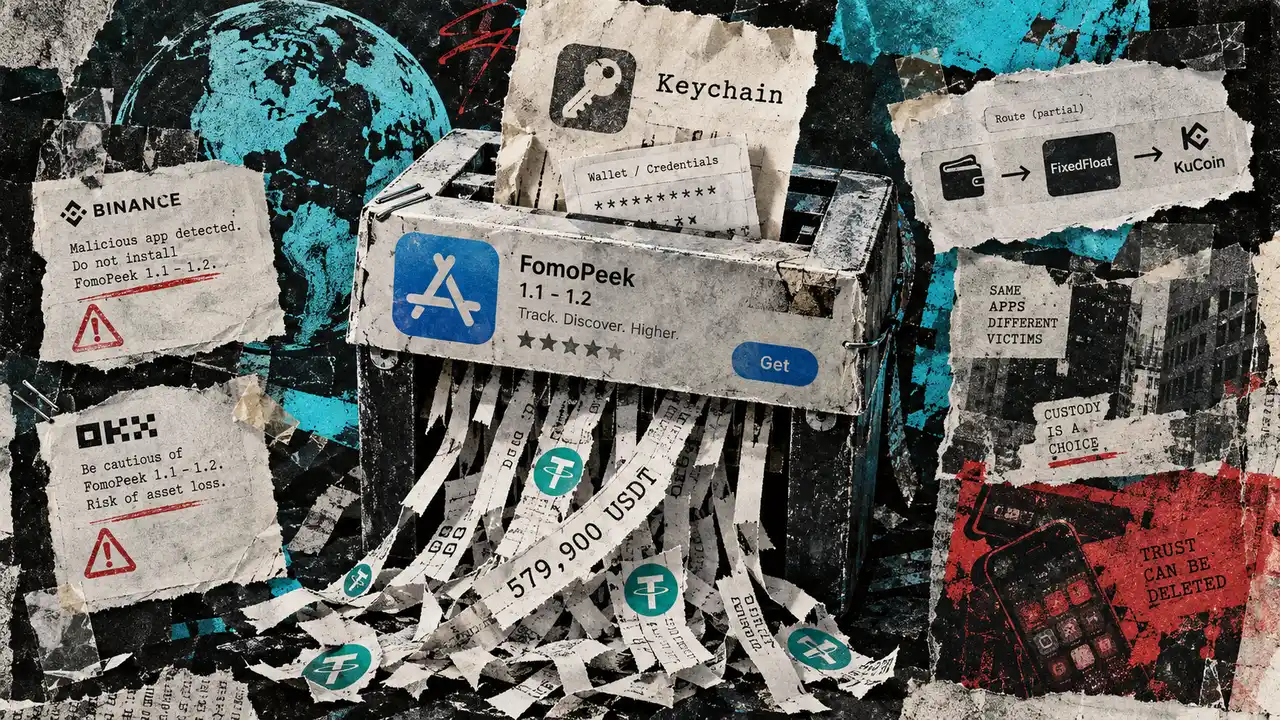
The app, called FomoPeek, contained two malicious modules capable of exploiting iOS vulnerabilities to gain elevated privileges and access Keychain data and files from other applications, SlowMist's investigation revealed.
The affected versions were released on September 9 and September 12. Version 1.3, released on September 17, removed the malicious components.
SlowMist conducted the investigation with the OKX security team after receiving reports from users who experienced asset theft and had previously installed the affected FomoPeek versions.
The exploit framework included eight attack methods and supported iOS versions ranging from 12.0 to 18.7.2 and 26.0 to 26.1.
According to SlowMist's onchain analysis, a primary hacker address associated with the incident received approximately 579,984 USDT. The address became active on September 15. The stolen funds moved across multiple blockchain networks before being consolidated and transferred through several addresses and services.
SlowMist identified that portions of the funds were transferred to services including FixedFloat, KuCoin and cce.cash, with other funds dispersed through additional addresses that the firm continued to trace.