Newly disclosed vulnerabilities in Eclair, a Bitcoin Lightning implementation, could cause unpatched nodes to crash repeatedly without requiring attackers to spend on-chain Bitcoin. The flaw affects reachable nodes running version 0.14.0 and earlier.
Persistent Crash Vulnerability Explained
Research published by Erick Cestari on Sept. 30 details how inconsistent checks of temporary and final channel identifiers allowed Eclair's peer limits to undercount unfunded channels. Malicious peers could accumulate saved requests without broadcasting funding transactions or paying on-chain fees.
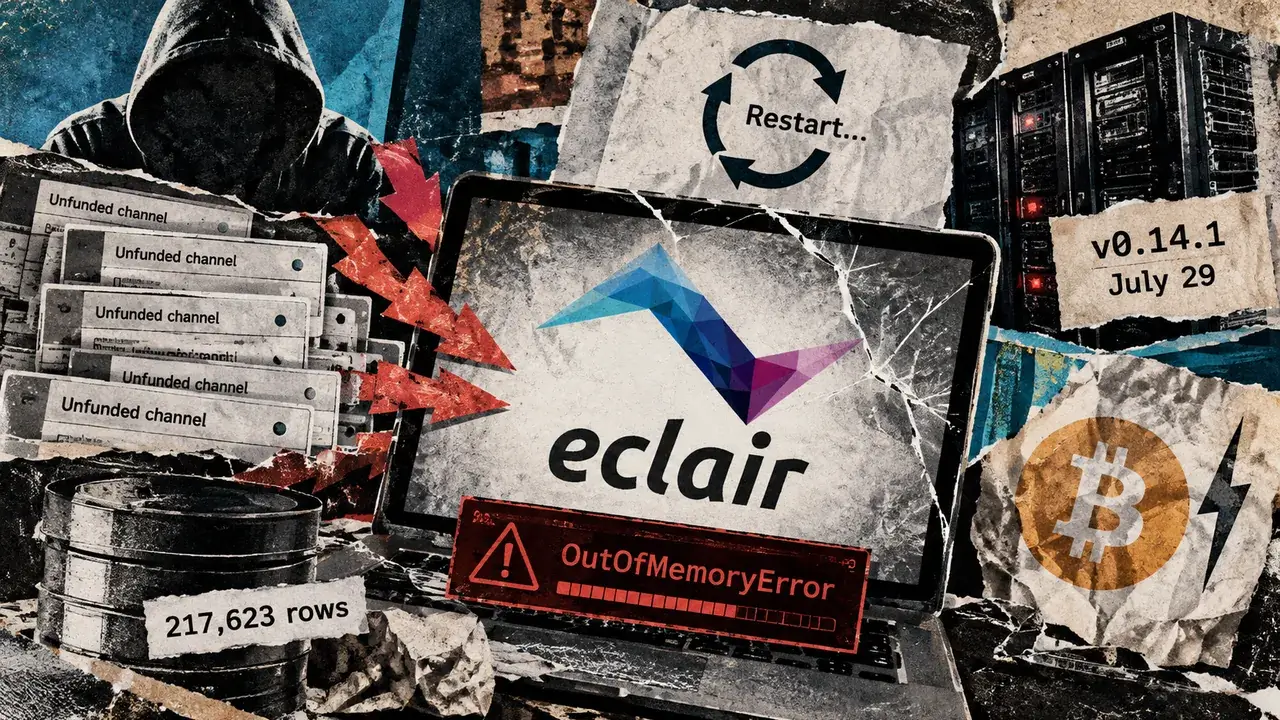
While the attack still required network traffic and computing resources, the BTC normally needed to fund a channel was not committed while memory and database costs accumulated on the vulnerable node. In a laboratory test using a 4 GB Java virtual machine heap, Eclair version 0.14.0 crashed after roughly 47 minutes with 217,623 rows saved in the channel database.
Because the records remained on disk after the initial crash, simply restarting the node failed to restore service. Eclair would reload the channels during startup and immediately exhaust memory again, requiring operators to manually remove fake records or increase heap space to recover.
Patches and Current Recommendations
ACINQ merged a patch strengthening duplicate-channel checks on July 17, and version 0.14.1 shipped on July 29 to address these denial-of-service findings. A second bug involving a channel-opening race condition was disclosed by Matt Morehouse / lnfuzz as LNF-2026-0003.
ACINQ now recommends upgrading to version 0.14.3, released on Sept. 14, to address separate vulnerabilities covered in previous security advisories. Preventing new unfunded-channel floods and recovering an already overloaded database remain distinct concerns for node operators.