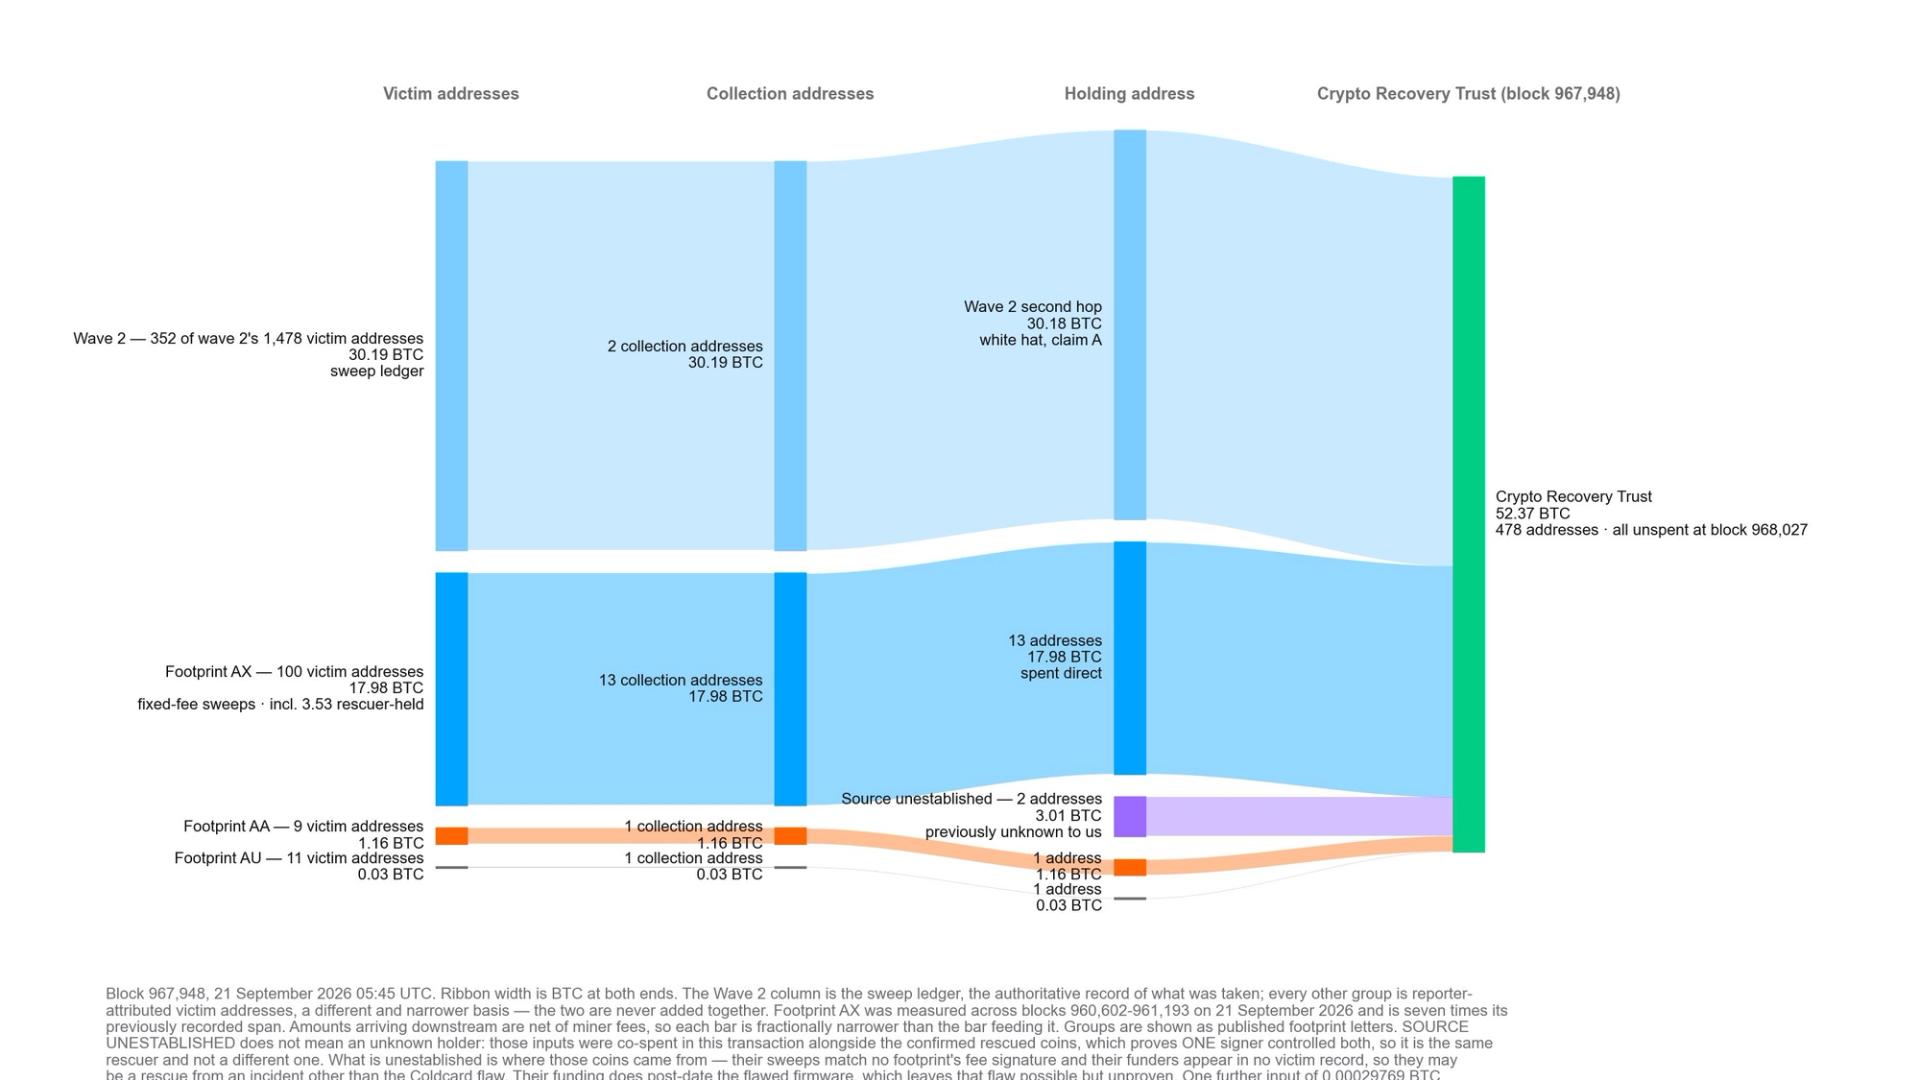
White-hat hackers have moved 52.37 bitcoin tied to the July Coldcard wallet exploit into an address associated with a newly formed recovery trust, according to Galaxy Digital's Head of Research Alex Thorn.
The Coldcard exploit began on July 30 with multiple waves of attacks in subsequent days, resulting in estimated losses exceeding $100 million. Attackers exploited a vulnerability that caused wallets to generate seeds using weak software-based randomness instead of the device's dedicated random number generator, making some seeds vulnerable to reconstruction by hackers.
Coinkite, the maker of Coldcard, has since patched the firmware, though funds already exposed under the old seeds remain at risk.
According to Thorn, not all funds moved from victim wallets were taken by malicious actors. Some were swept by white-hat security professionals—ethical hackers who use their skills to secure assets and fix vulnerabilities. The 52.37 bitcoin moved this week represents such a sweep, consolidated from Wave 2 of tracked exploit funds and sent to an address carrying an OP_RETURN message reading "claim:cryptorecoverytrust dot com."
Thorn said the amount represents 2.8% of total tracked exploit funds, with roughly 40% of Wave 2 identified as whitehat activity. An additional 3.0134 bitcoin with no prior tracking history also flowed into the recovery trust address in the same transaction, which Thorn said is presumably additional white-hat-recovered Coldcard funds, though unconfirmed.
Victims can check whether their funds were recovered by visiting cryptorecoverytrust.com and searching their wallet addresses.