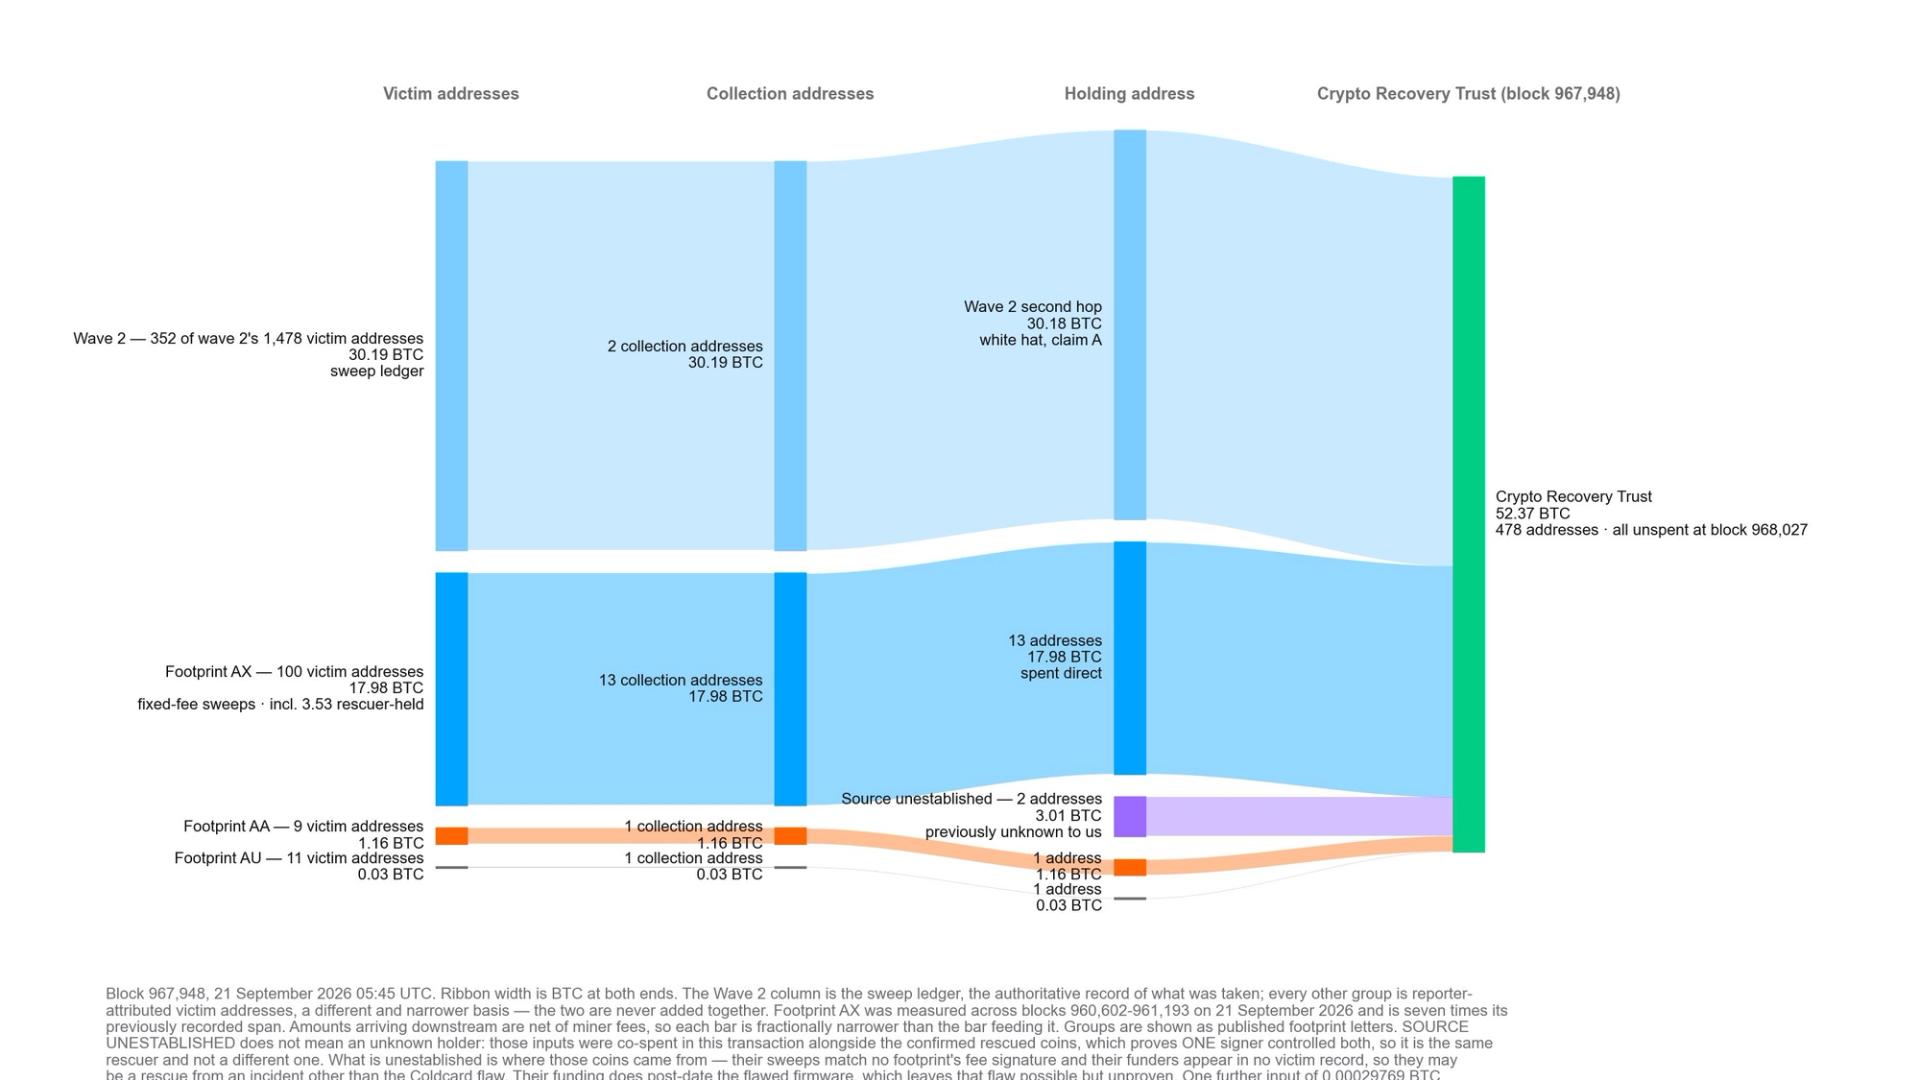
White hat security researchers have transferred bitcoin stolen through a Coldcard hardware wallet vulnerability to Crypto Recovery Trust, a Wyoming trust established to help return funds to victims, according to Galaxy Digital's Alex Thorn.
A total of 52.37 bitcoins, valued at approximately $4.5 million, were moved to the trust-controlled address. Thorn noted this represents 2.8% of the total funds compromised in the exploit.
The attacks began on July 31, targeting users of Coinkite's Coldcard hardware wallet. The company identified a firmware bug that caused the device's seed generation to revert to a weak software pseudorandom number generator instead of its hardware-based true random number generator, potentially allowing attackers to predict user seed phrases.
Galaxy Digital tracked the broader attack and found that 1,789.28 bitcoins were stolen across all incidents, totaling approximately $154.1 million at current prices.
Nick Bax of UMP Labs disclosed earlier this month that he participated in rescuing approximately 50 bitcoins that were at immediate risk of theft due to the Coldcard entropy flaw. Bax confirmed the funds are held by the Wyoming trust pending return to rightful owners.
Coinkite acknowledged in a statement that the bug "silently went unnoticed" and "its potential impact grew with every release" of affected software versions. The company subsequently urged users to update their software or relocate funds from the hardware wallet.
Following the exploit, some users have transferred their holdings to alternative storage solutions, including cryptocurrency exchanges.